Nexora Consulting Case Study
Enterprise Privacy Architecture in 6 Acts
A complete end-to-end Zero-Trust privacy governance implementation — from identity provisioning to live DLP blocking, Copilot AI guardrails, and statutory DSAR fulfillment across two regulatory jurisdictions.
01
Act 1 · Screenshots 01–05
Identity Foundation & Zero-Standing-Privilege Security
Legal & Security Challenge: Under DPDP Act Section 8(5) and Australian APP 11, data fiduciaries must enforce technical safeguards against unauthorized internal access. Standing administrative rights create a critical insider-risk exposure.
01
Workforce Directory Provisioning: Provisioned 26 directory identities across Nexora's Indian and Australian teams, separating regular business analysts from dedicated privacy leadership (DPO) and break-glass recovery accounts.
02–03
Role-Based Security Groups (12 Groups): Replaced individual user permissions with 12 role-segmented Entra Security Groups — SG-NEX-All-Employees, SG-NEX-Legal-Compliance, SG-NEX-Privacy-Operations, SG-NEX-IT-Security, SG-NEX-Finance, SG-NEX-HR, and more — so governance policies scale cleanly by department.
04
Just-In-Time Privilege Elevation (Entra PIM): Enforced zero standing privileges for Nexora's Data Protection Officer. Rather than holding permanent admin rights during routine work, the DPO holds Eligible assignments for Azure Information Protection Administrator and Compliance Administrator — activated only when needed with MFA and business justification.
05
Out-of-Band Break-Glass Isolation: Isolated Global Administrator strictly as a dedicated emergency recovery account, separated from day-to-day privacy and compliance administration — zero routine usage.
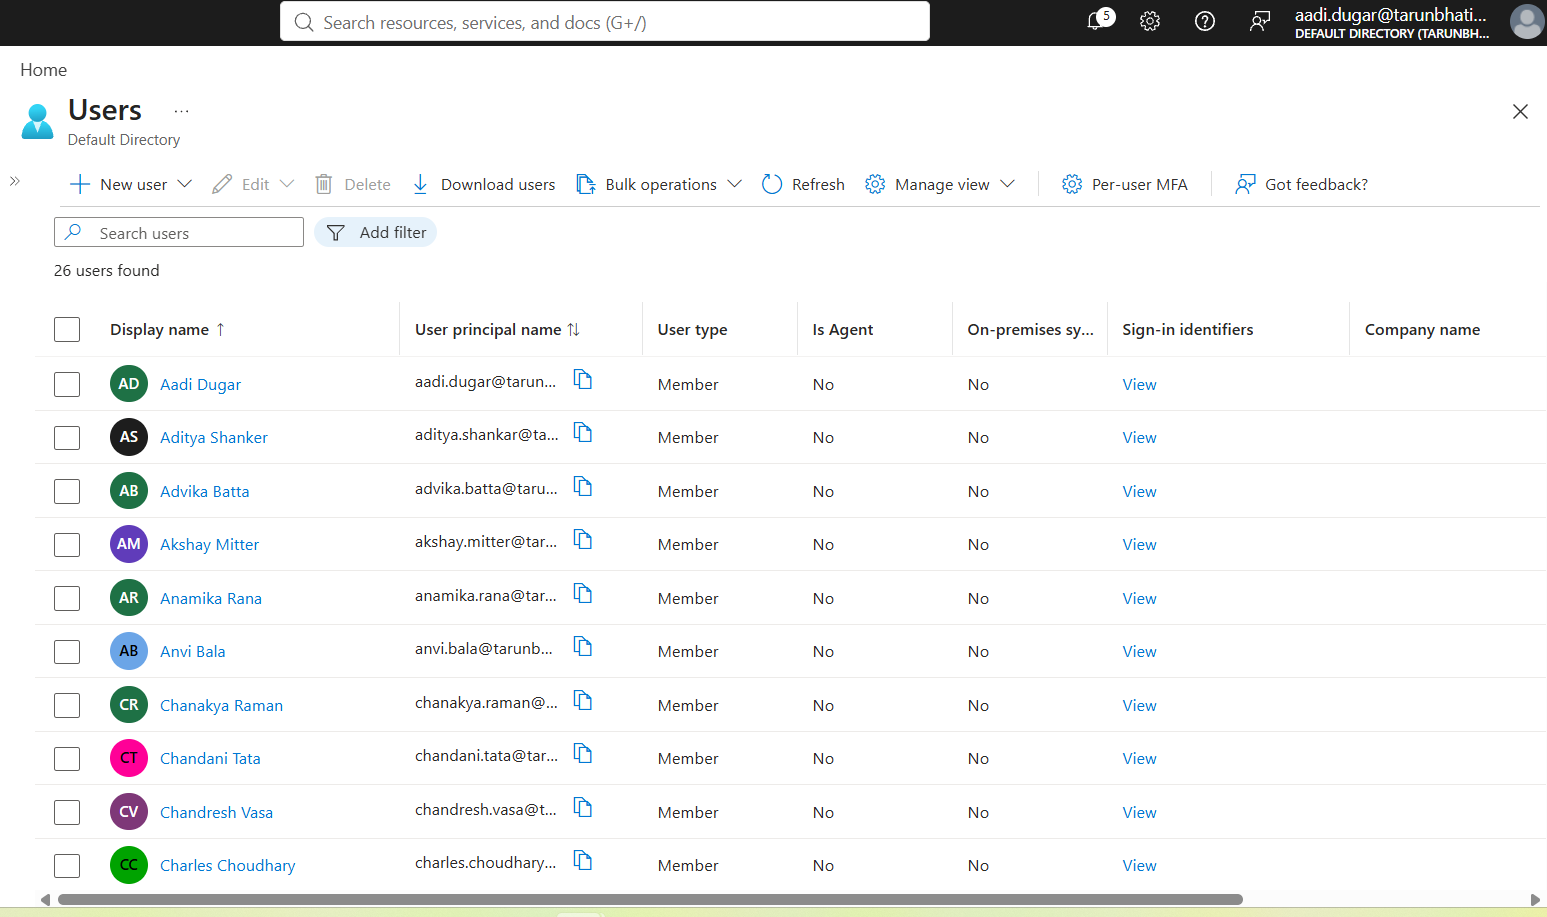
01 — Workforce Directory (26 Users)
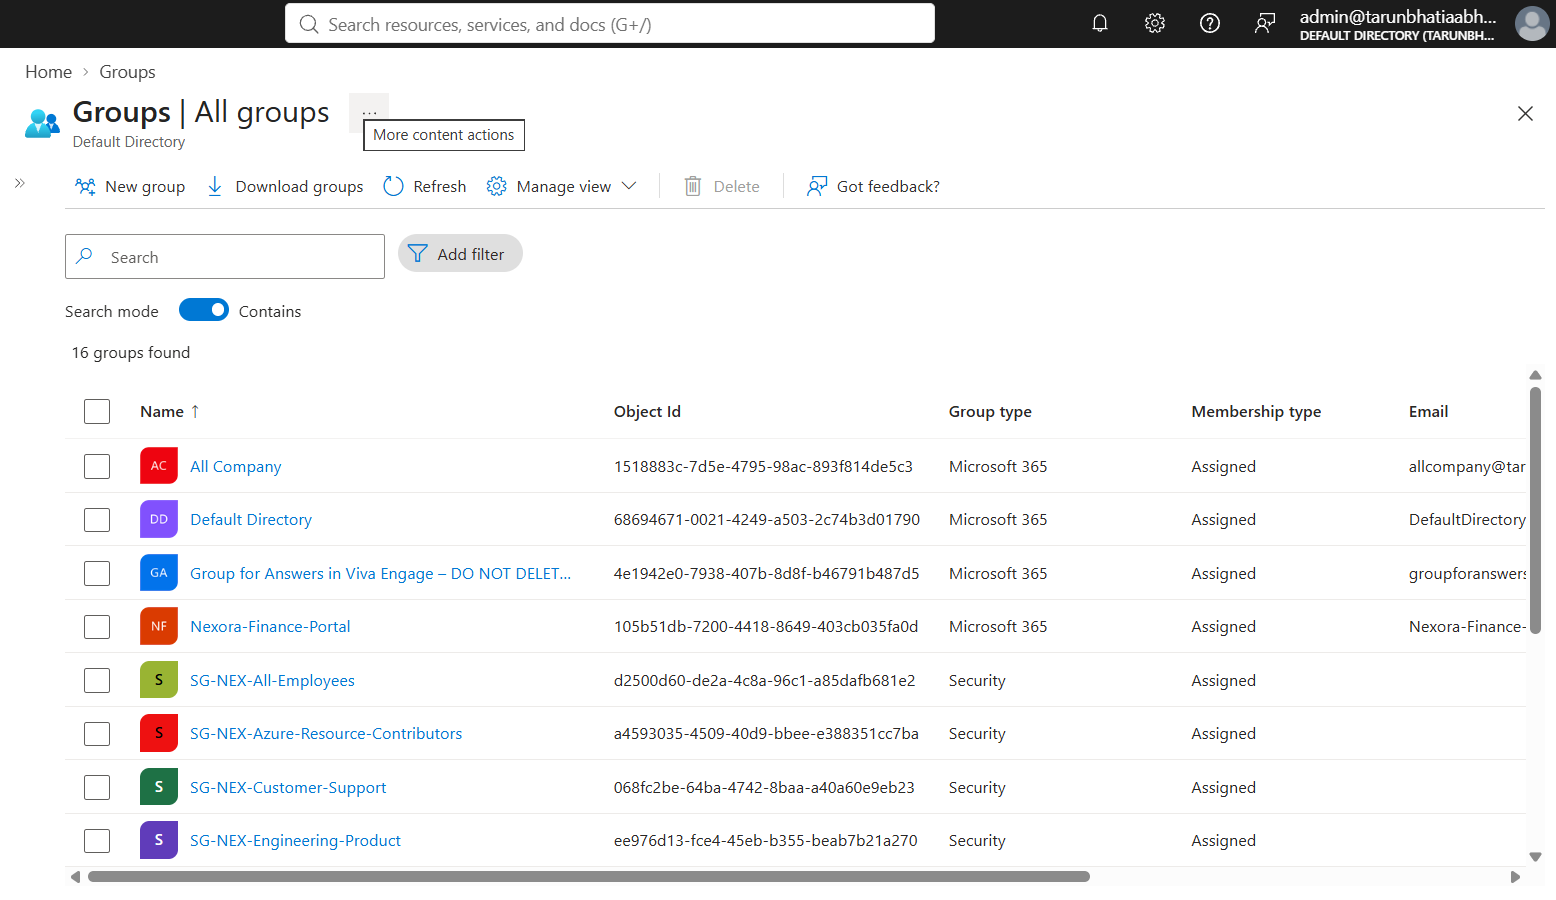
02 — Security Groups (1/2)
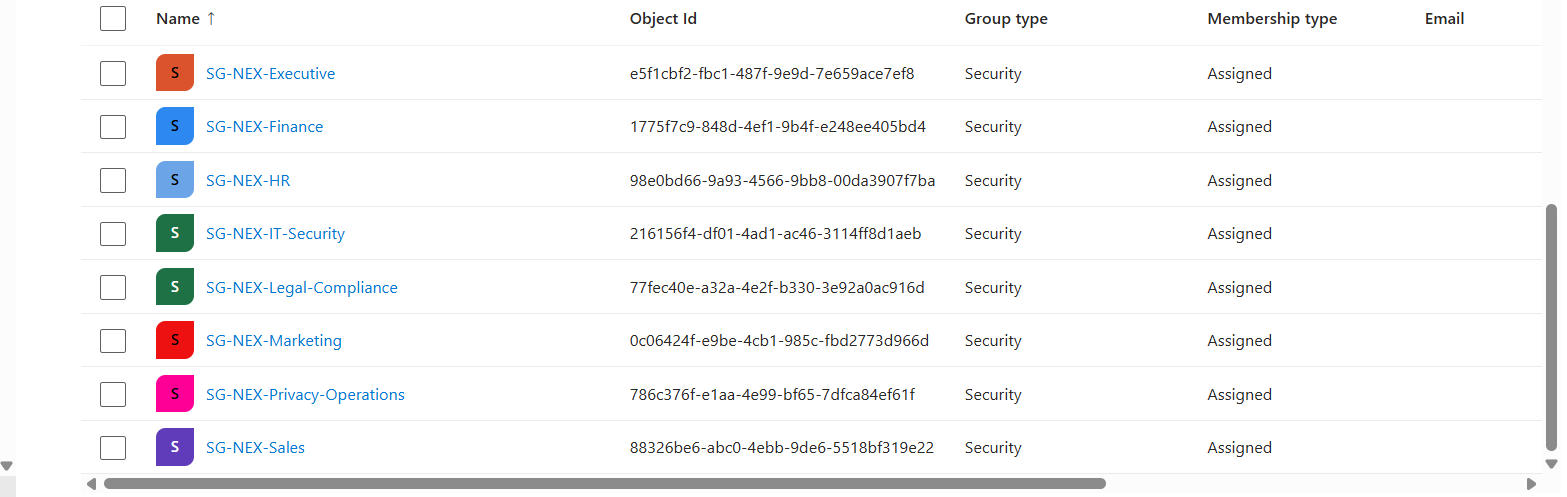
03 — Security Groups (2/2)
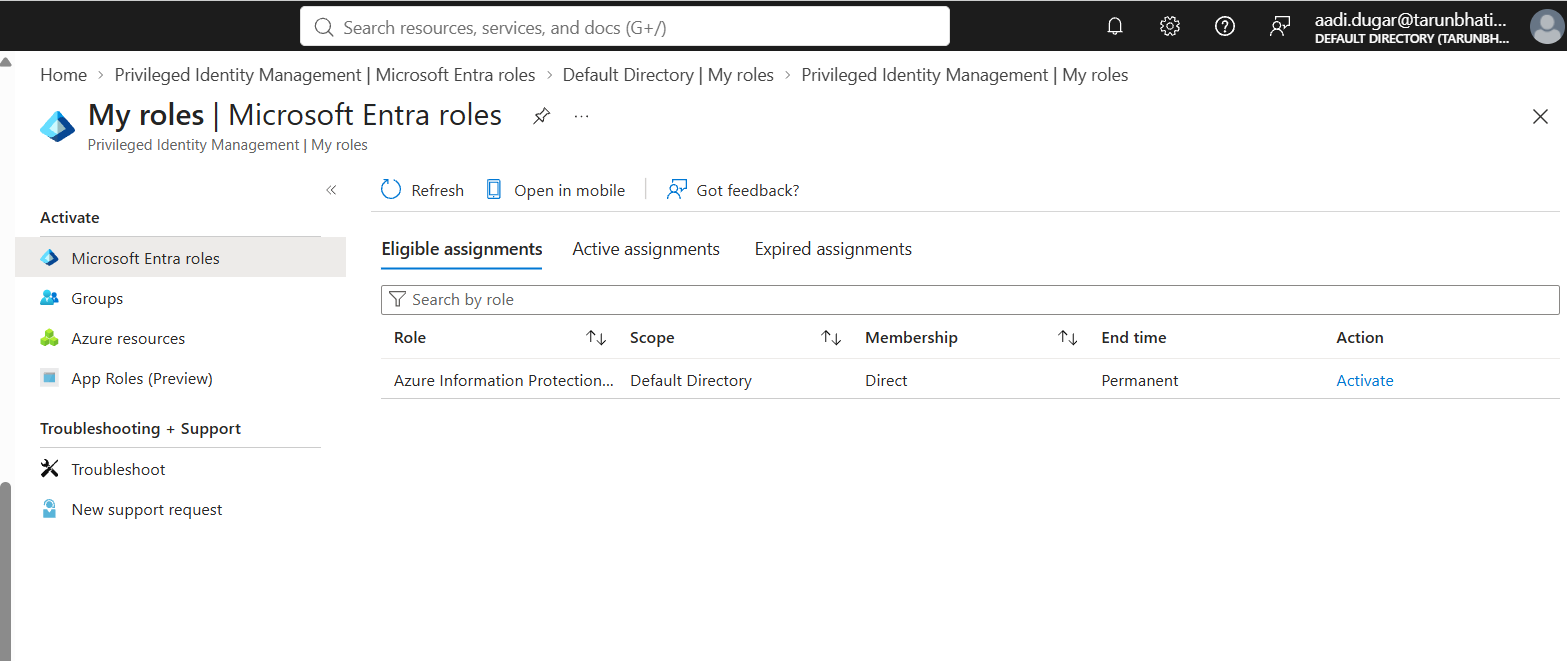
04 — PIM JIT Elevation
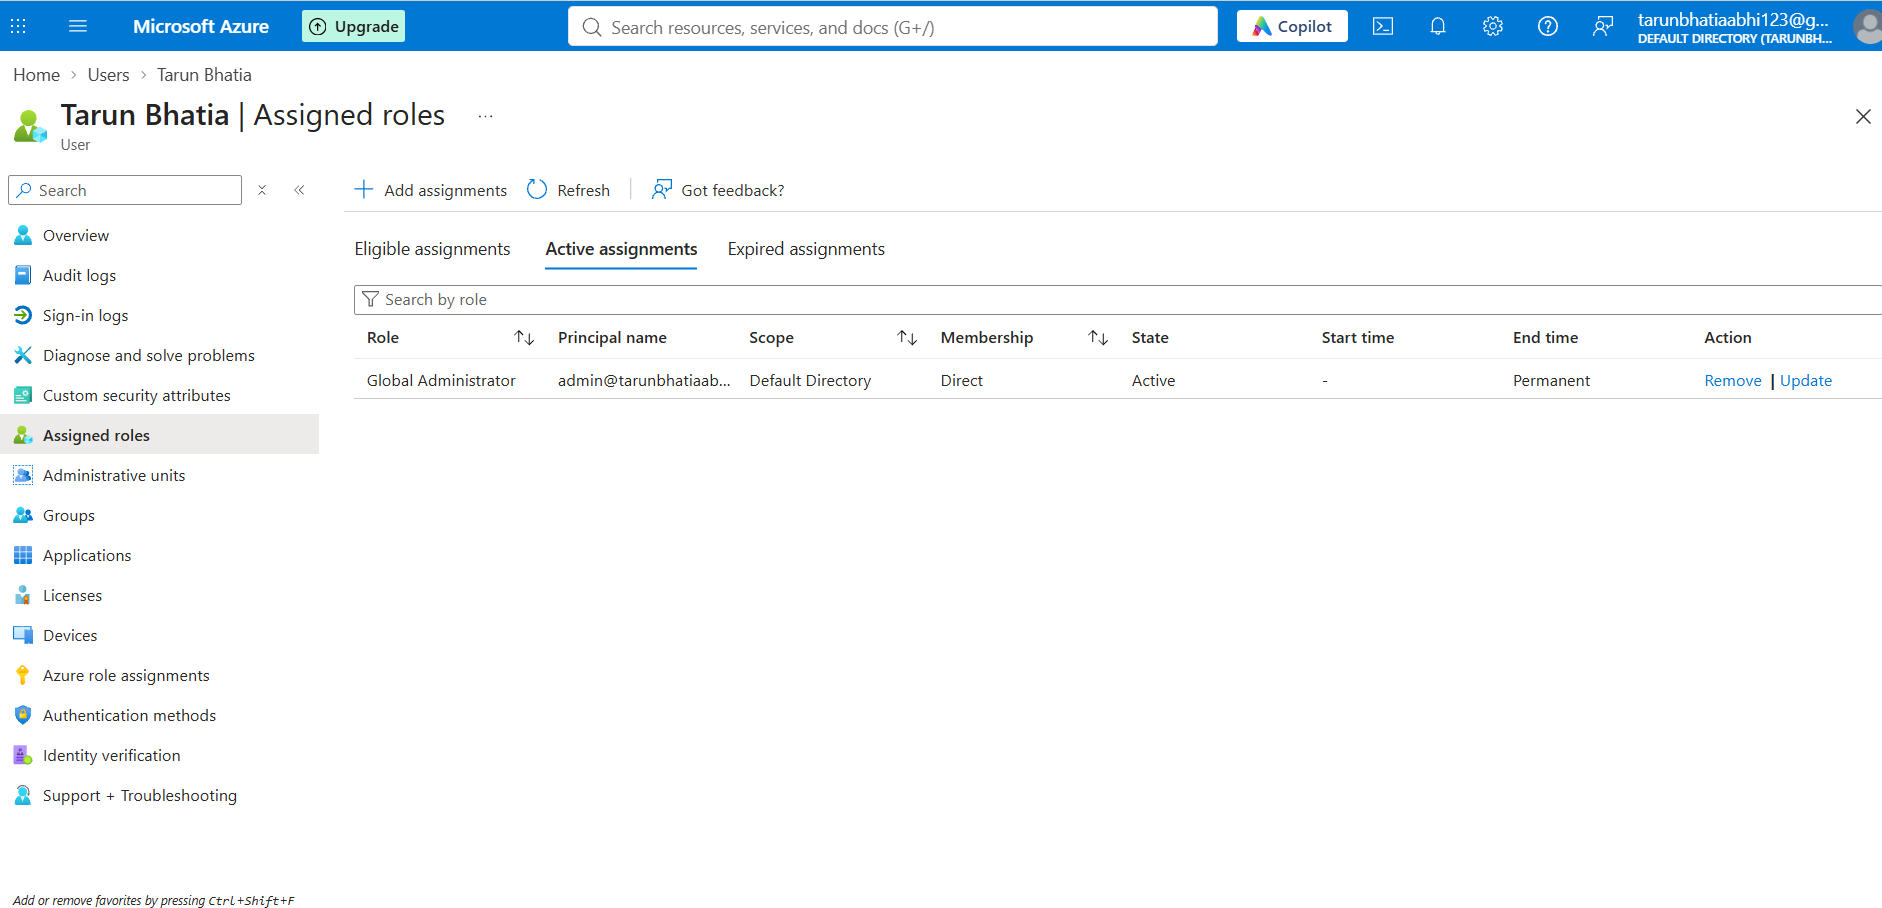
05 — Break-Glass Admin
02
Act 2 · Screenshots 06–10 + 30
Cloud Data Residency & Hierarchical Azure RBAC
Legal & Security Challenge: Cross-border consulting firms must demonstrate regional data sovereignty and ensure storage administrators cannot arbitrarily read confidential HR or Finance datasets.
06–07
Central India Data Sovereignty: Deployed Nexora's entire governance infrastructure inside Central India (
rg-nexora-privacy-lab-dev-001), encompassing the Microsoft Purview governance account (purview-nexora-gov-001), segregated Finance and HR storage accounts (stnexorafinance001, stnexorahrdev001), and Azure SQL (sql-nexora-dev-001).08
Purview Governance Plane RBAC: Locked down administrative control over
purview-nexora-gov-001 so security auditors can inspect governance posture without altering classification rules.09–10
Hierarchical Least-Privilege Storage IAM: Applied two-tier RBAC separation on
stnexorafinance001. At the storage-account level: read-only metadata visibility. At the finance-documents container level: SG-NEX-Finance holds Storage Blob Data Contributor for uploads, while SG-NEX-Privacy-Operations and Purview's System-Assigned Managed Identity are restricted to Storage Blob Data Reader.30
KQL Audit — All 11 RBAC Assignments Verified: Instead of manually clicking through 5 different Azure panels, wrote a Kusto Query Language (KQL) query in Azure Resource Graph Explorer to pull every RBAC role assignment across the subscription into one audit table — proving least-privilege access in seconds.
authorizationresources
| where type == "microsoft.authorization/roleassignments"
| extend principalId     = tostring(properties.principalId),
         principalType   = tostring(properties.principalType),
         roleDefinitionId = tostring(properties.roleDefinitionId),
         scope            = tostring(properties.scope)
| join kind=leftouter (
    authorizationresources
    | where type == "microsoft.authorization/roledefinitions"
    | extend roleDefinitionId = id,
             roleName = tostring(properties.roleName)
) on roleDefinitionId
| project scope, principalId, principalType, roleName
| order by scope asc
KQL Output — All 11 Verified RBAC Assignments
| Scope Level | Identity / Group | Azure RBAC Role | Security Purpose |
|---|---|---|---|
| Subscription | Tarun Bhatia (Break-Glass Owner) | Owner | Emergency subscription governance |
| Resource Group | purview-nexora-gov-001 (Managed Identity) | Storage Blob Data Reader | Keyless Purview scan access across all storage |
| Resource Group | admin@... (Tenant Admin) | Reader | Read-only infrastructure visibility |
| Storage Account | SG-NEX-Finance | Reader | Management-plane only (no blob read) |
| Storage Account | SG-NEX-Privacy-Operations | Reader | Management-plane only (no blob read) |
| Container (finance-docs) | SG-NEX-Privacy-Operations | Storage Blob Data Reader | Read-only privacy audit inspection |
| Container (finance-docs) | SG-NEX-Finance | Storage Blob Data Contributor | Write/upload — Finance container ONLY |
| Storage Account (HR) | SG-NEX-Privacy-Operations | Reader | Management-plane only (no blob read) |
| Storage Account (HR) | SG-NEX-HR | Reader | Management-plane only (no blob read) |
| Container (hr-docs) | SG-NEX-Privacy-Operations | Storage Blob Data Reader | Read-only HR privacy audit |
| Container (hr-docs) | SG-NEX-HR | Storage Blob Data Contributor | Write/upload — HR container ONLY |
Strict Departmental Silos: SG-NEX-HR can only write to
hr-documents — zero access to finance-documents. SG-NEX-Finance can only write to finance-documents — zero access to hr-documents.Privacy Oversight Without Tampering: SG-NEX-Privacy-Operations can inspect both containers (Reader) but cannot alter or delete any business records.
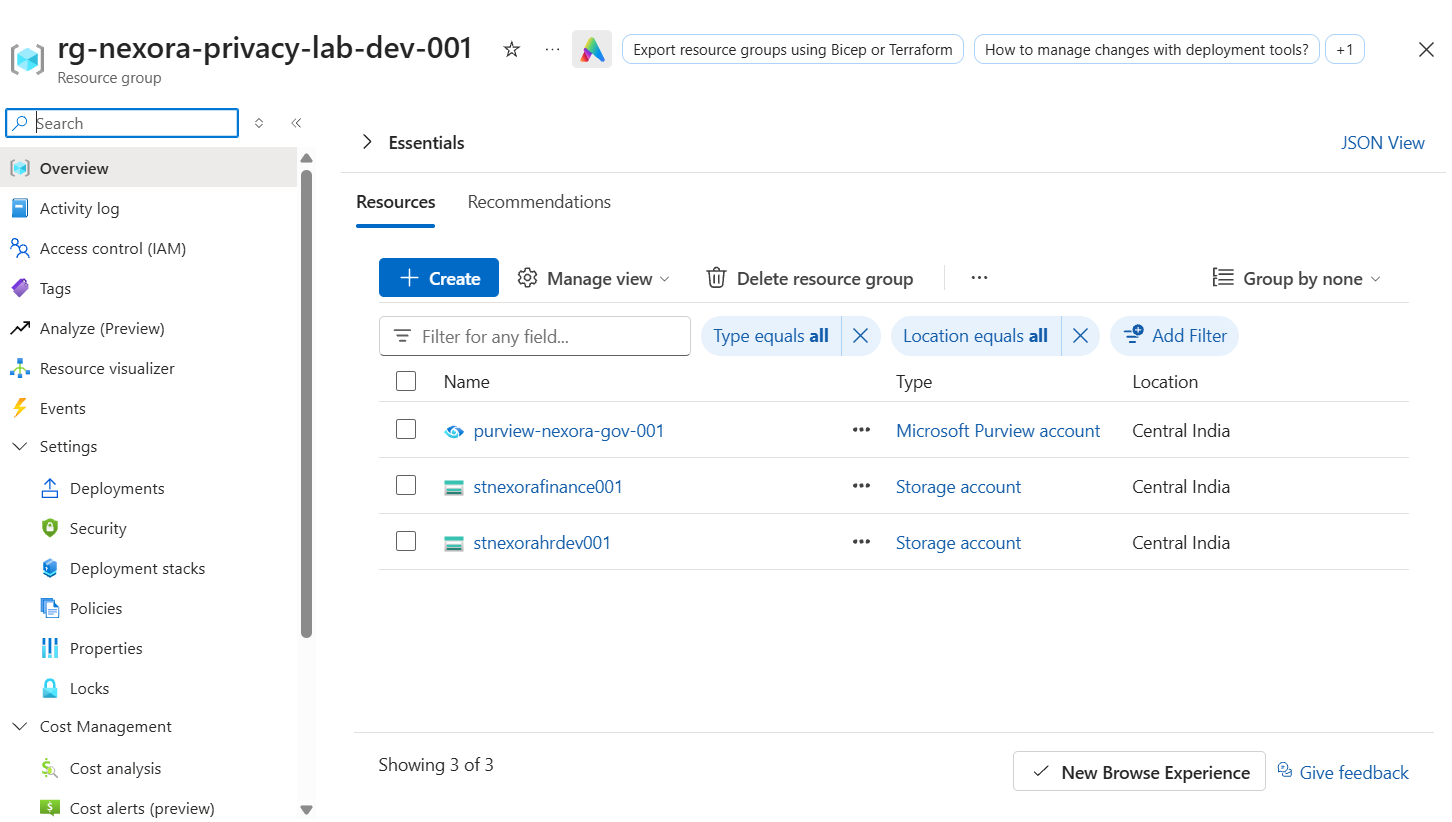
06 — Resource Group (Central India)
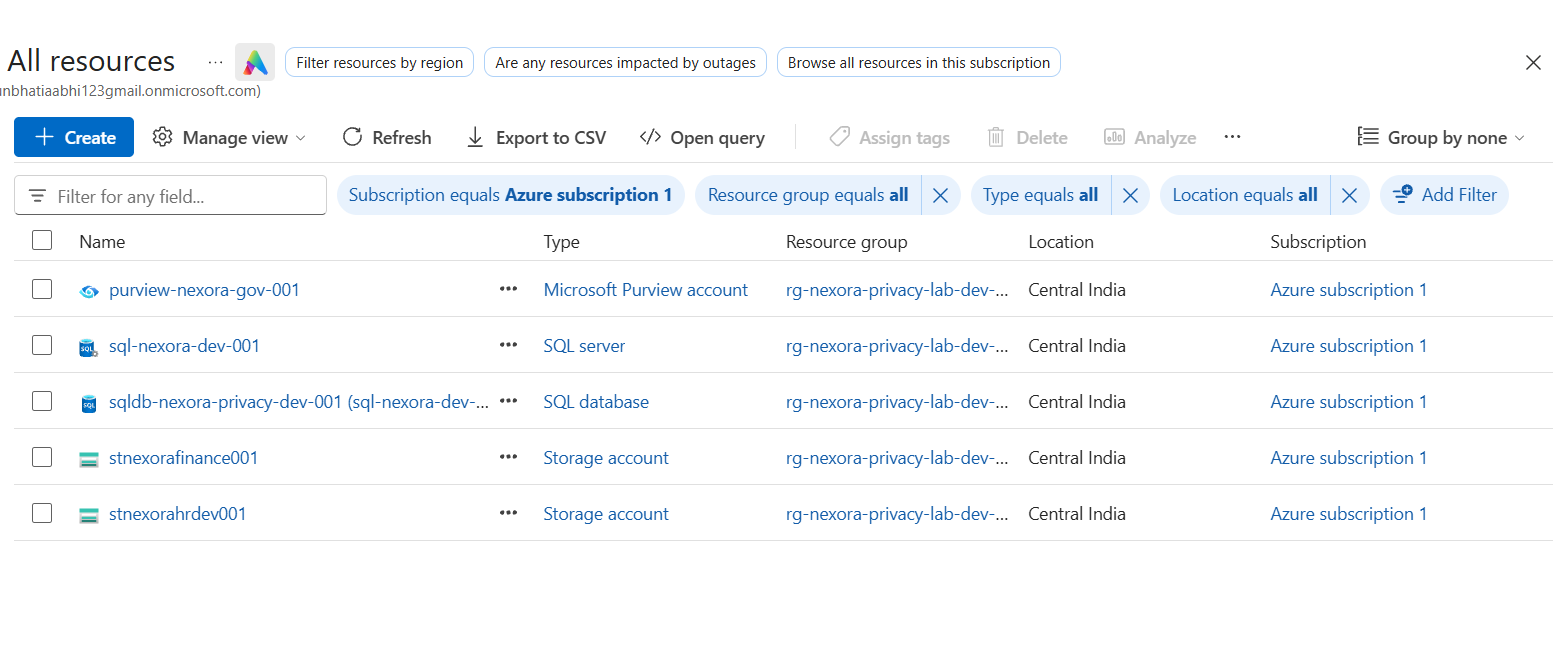
07 — All Cloud Resources
08 — Purview RBAC
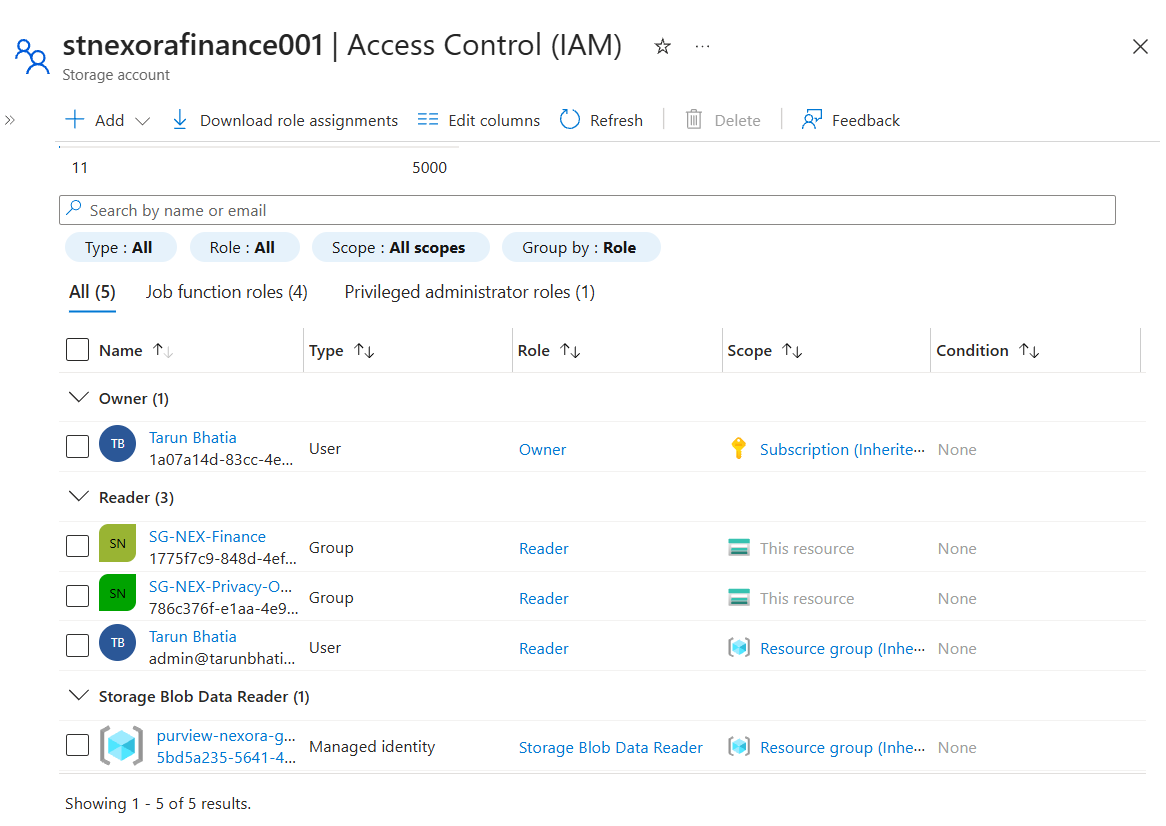
09 — Storage Account RBAC
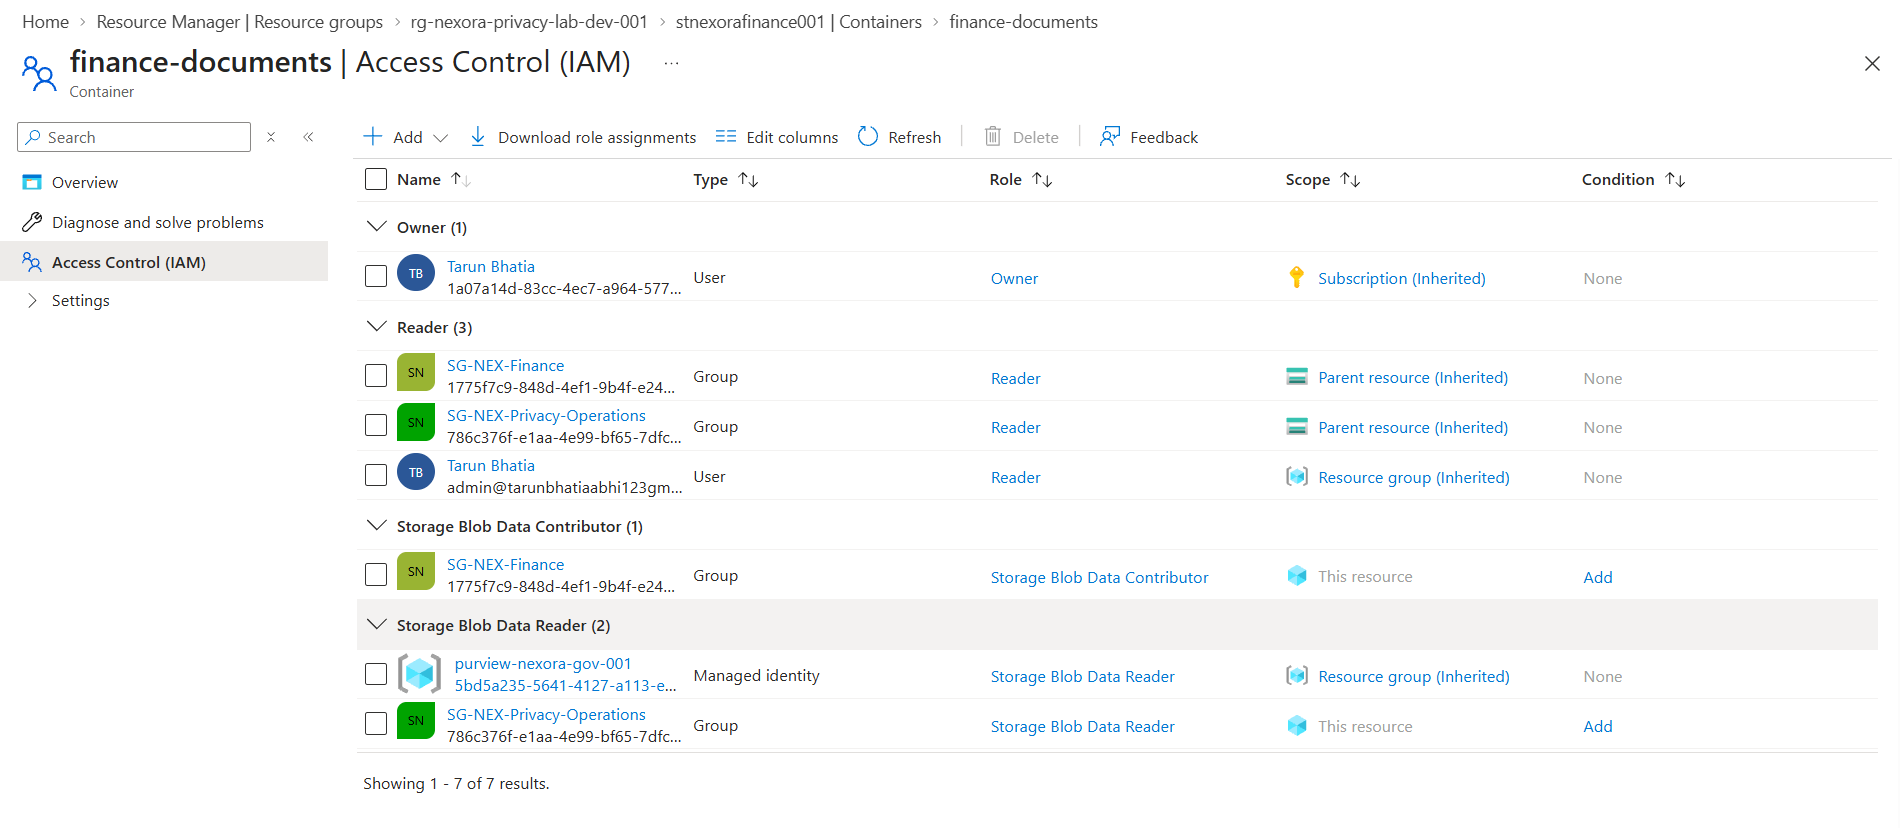
10 — Container-Scoped RBAC
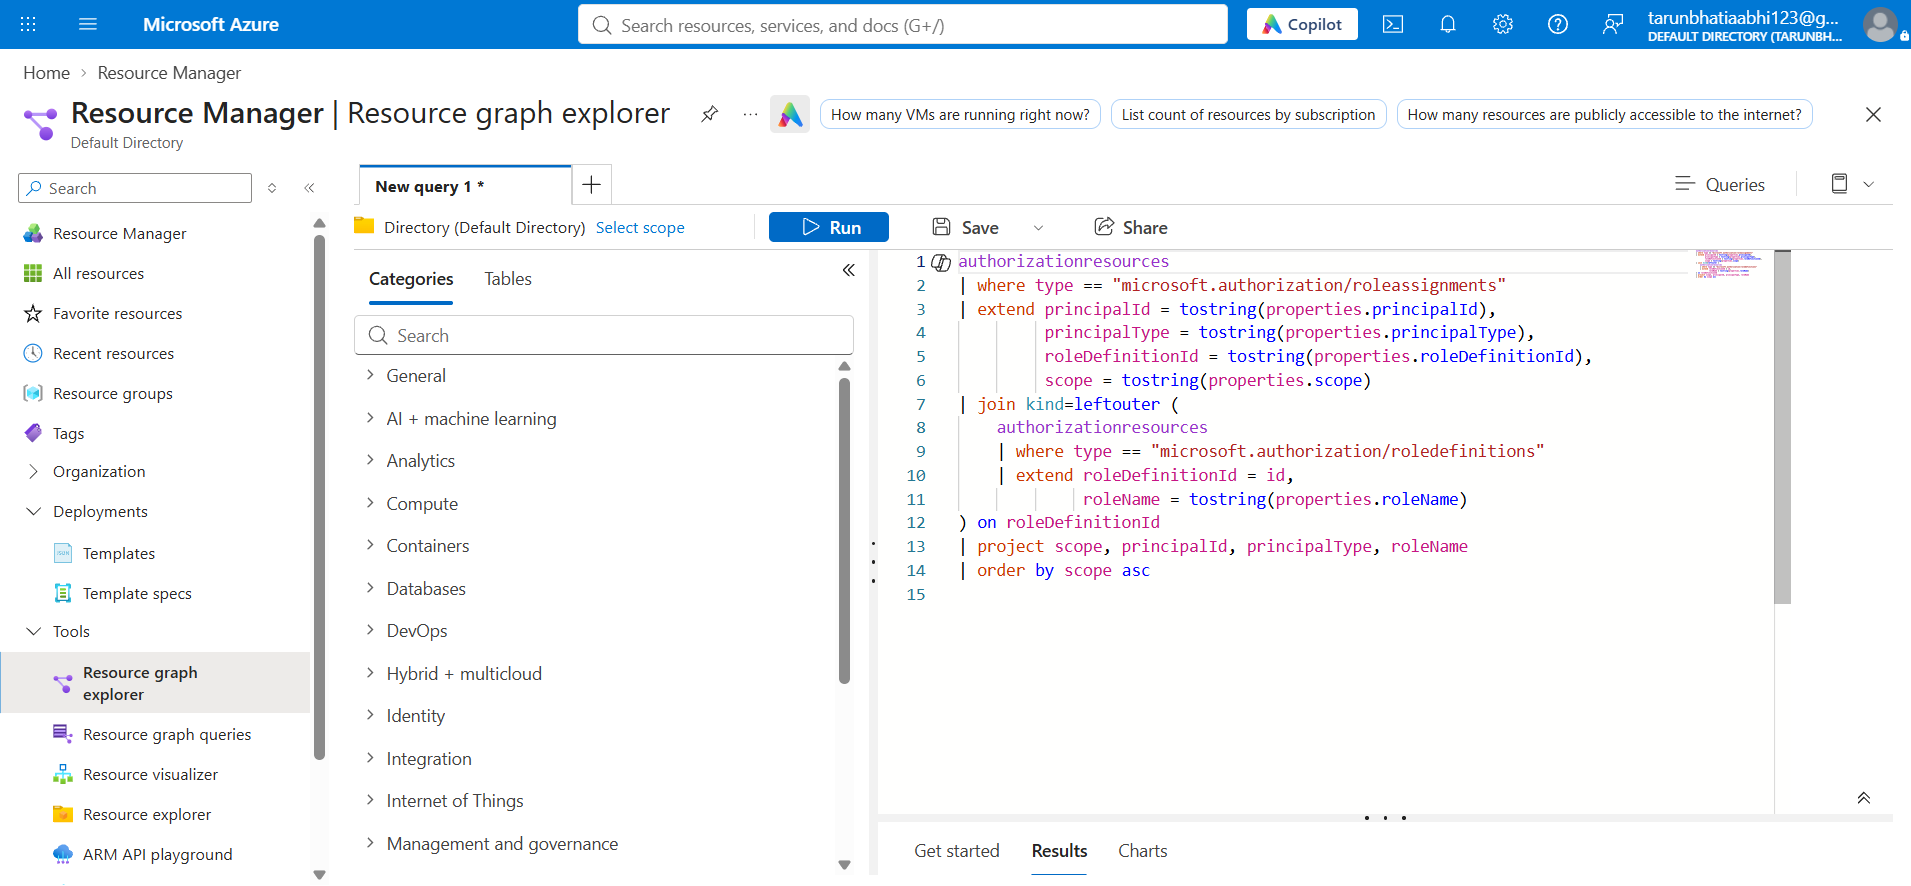
30 — KQL RBAC Audit
03
Act 3 · Screenshots 11–15
Automated Data Discovery & PII Classification
Legal & Security Challenge: Organizations cannot protect personal data they cannot locate. Manual data-inventory spreadsheets rapidly go stale as new vendor and payroll files are uploaded.
11–12
Private Data Lake Staging: Disabled anonymous public access on
finance-documents and staged realistic financial and vendor datasets — bank_reconciliation.csv, card_transactions_test_only.csv, invoice_register.csv, vendor_master.csv.13
Keyless Managed Identity Registration: Registered Azure Blob Storage inside Microsoft Purview Data Map using System-Assigned Managed Identity authentication — eliminating hardcoded storage keys or shared access signatures entirely.
14–15
Automated Column-Level PII Detection: Executed automated scans that indexed every CSV into Purview Unified Catalog and automatically classified India Permanent Account Number (PAN) (
Beneficiary_PAN_TEST) and financial identifiers inside bank_reconciliation.csv.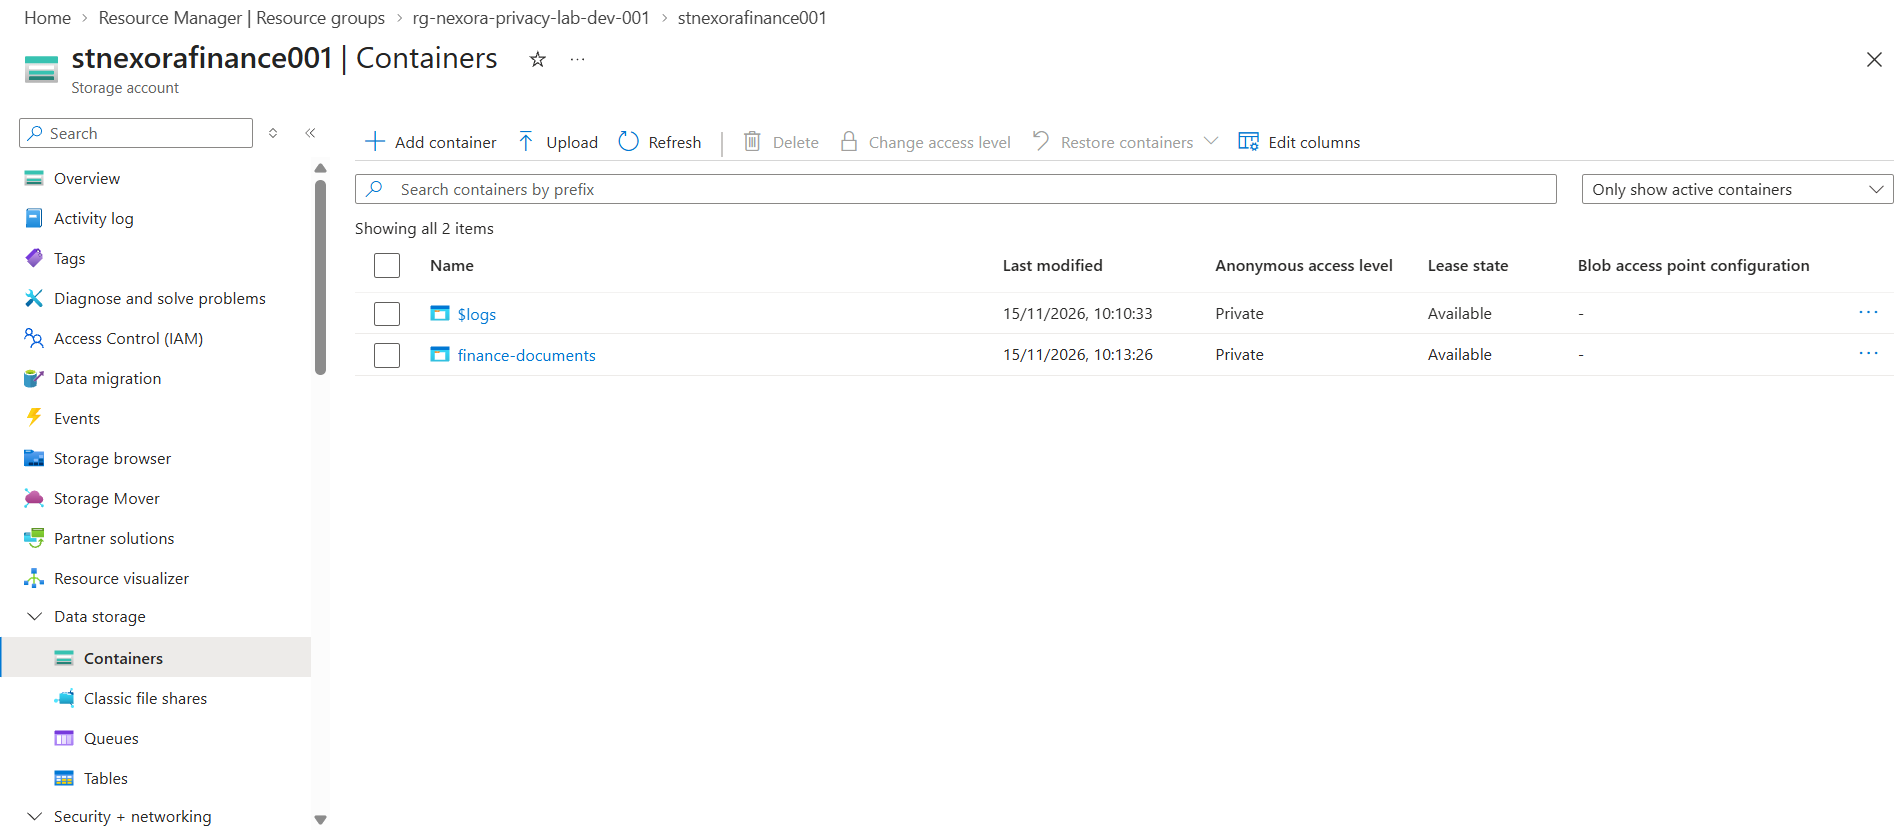
11 — Private Blob Container
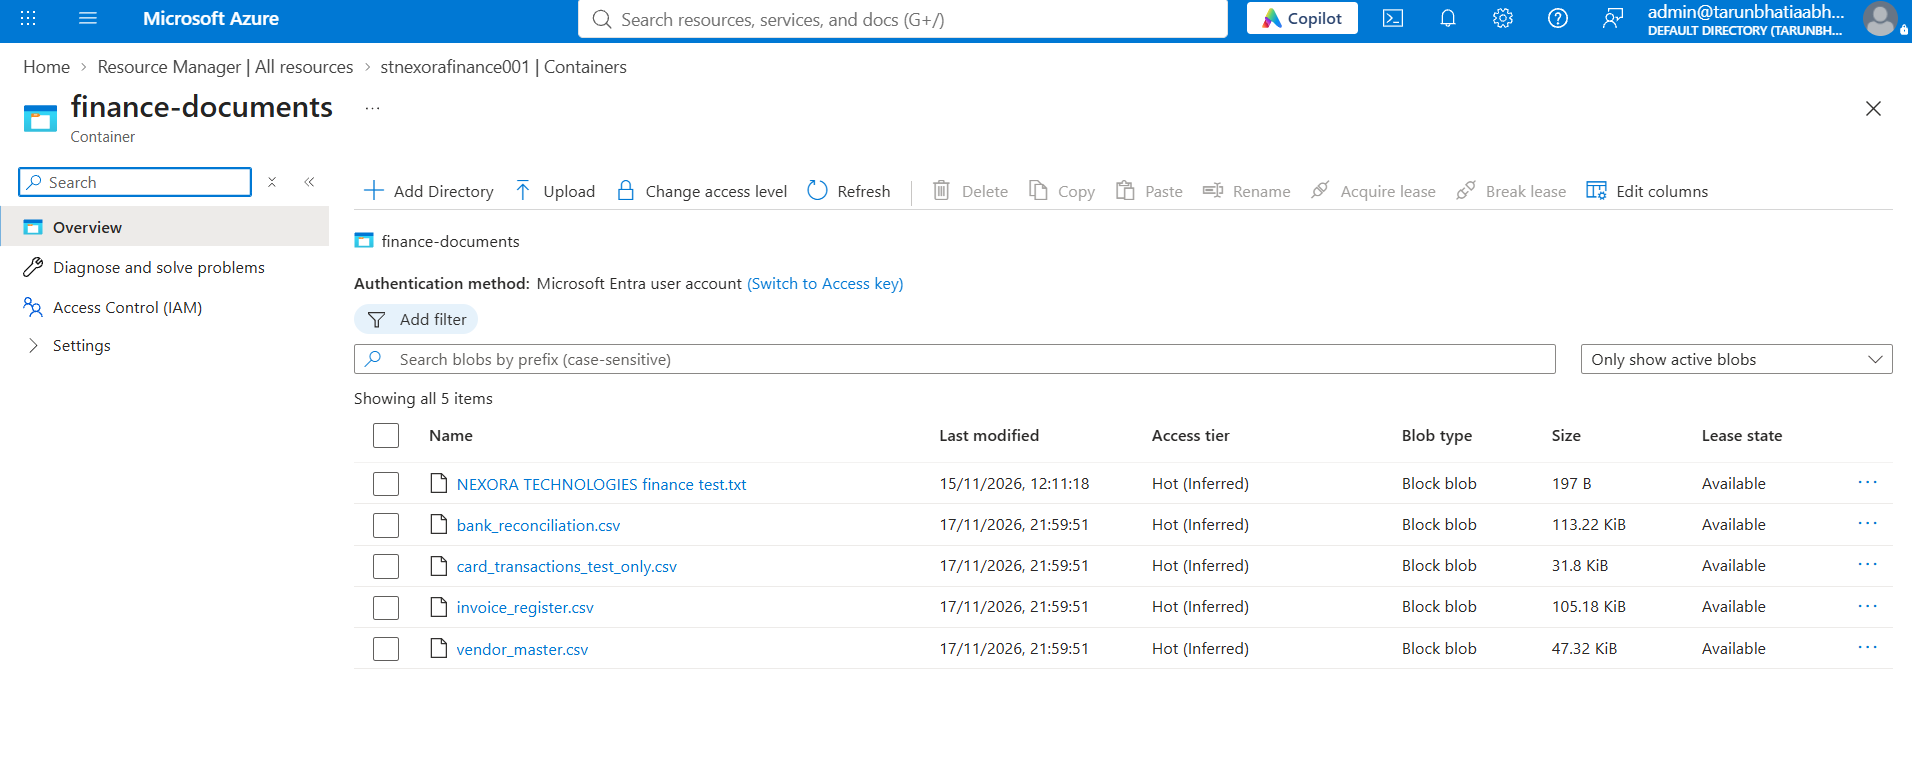
12 — Staged Financial Datasets
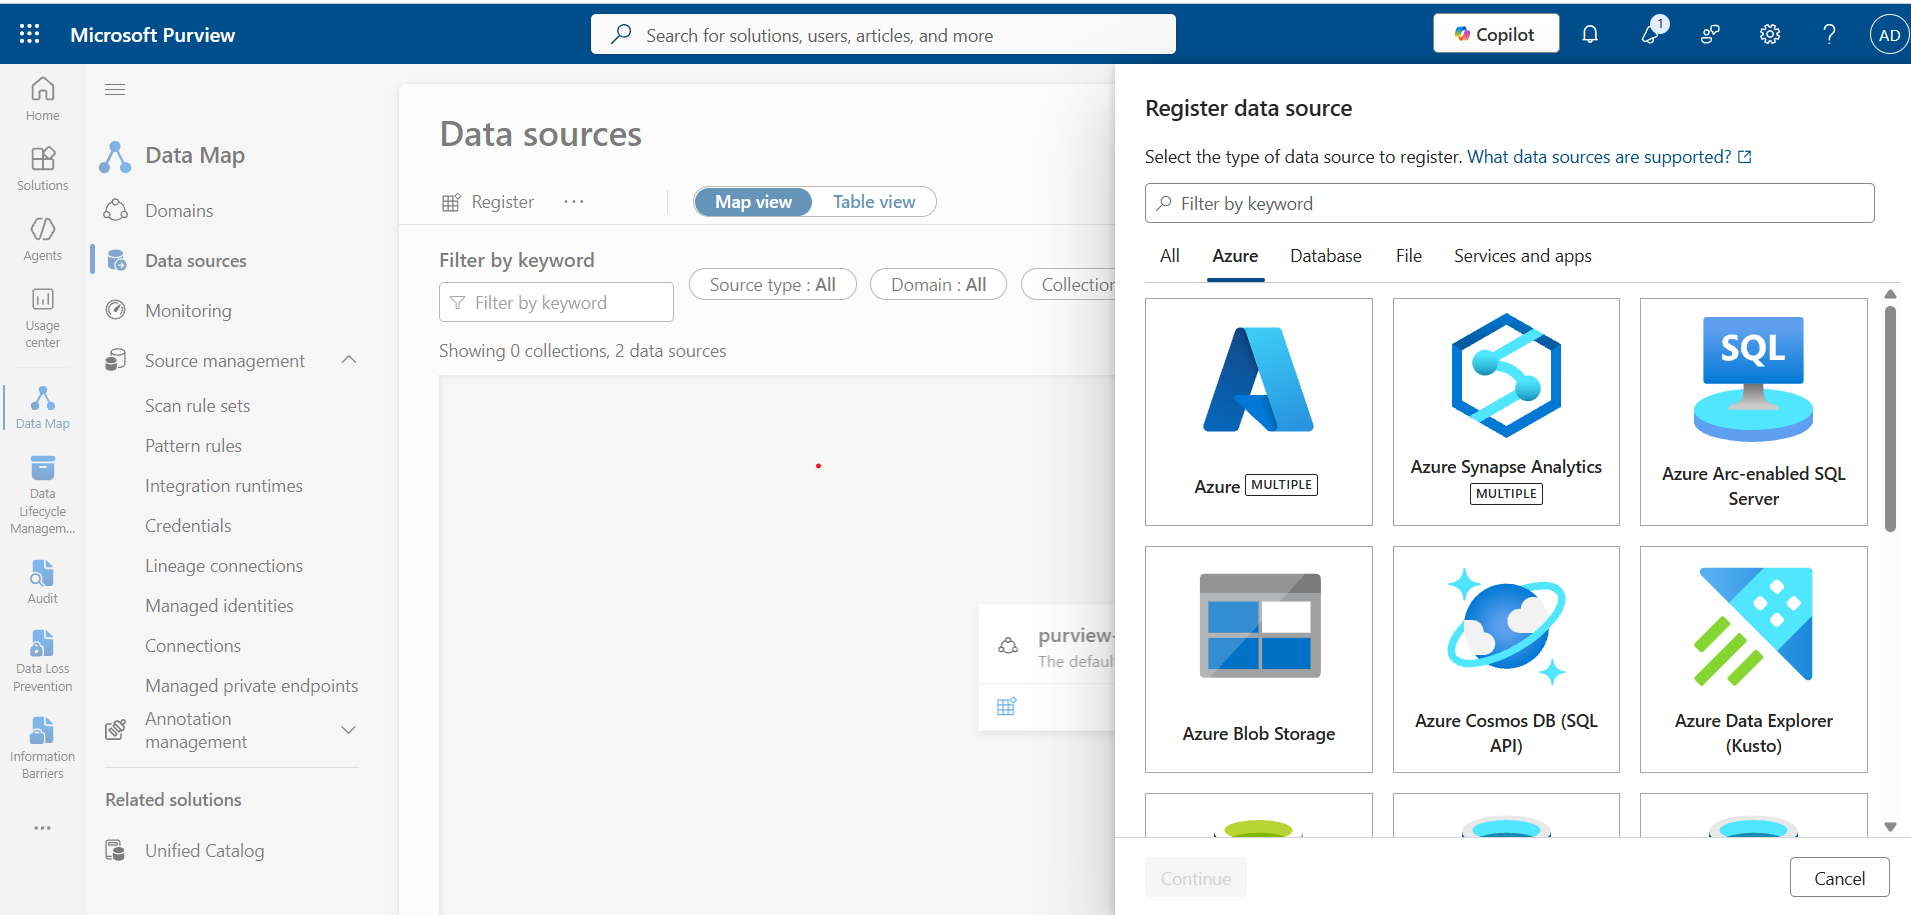
13 — Data Map Registration
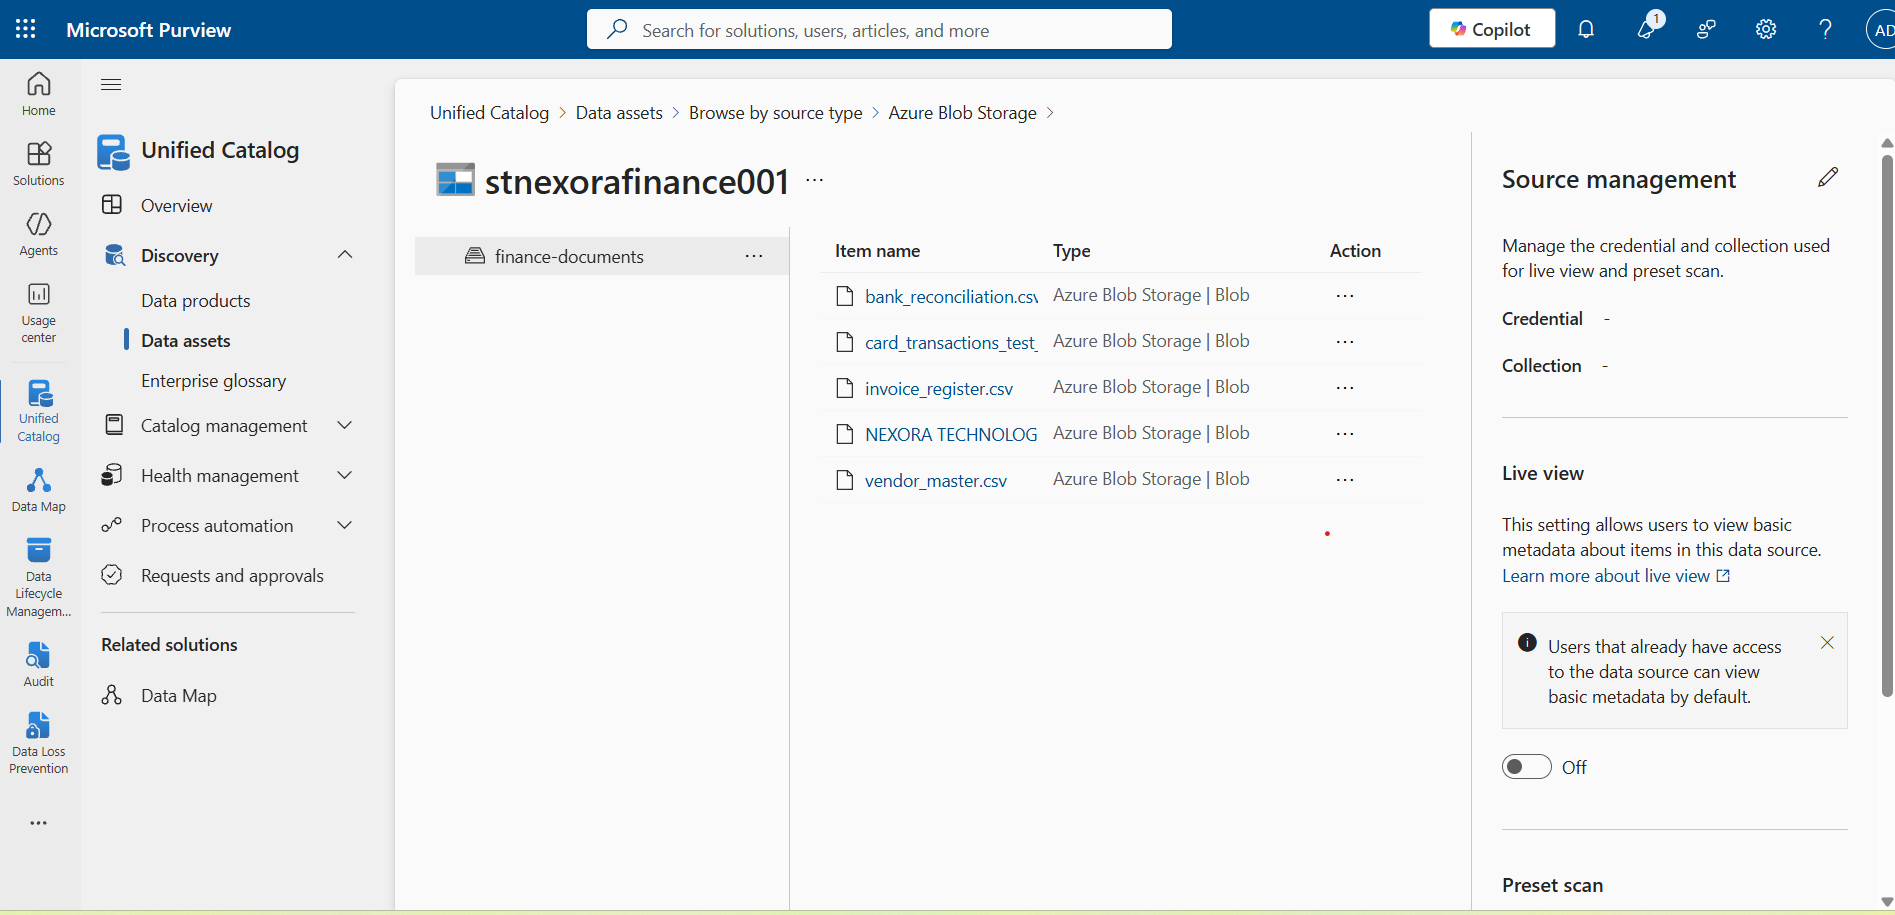
14 — Unified Catalog Assets
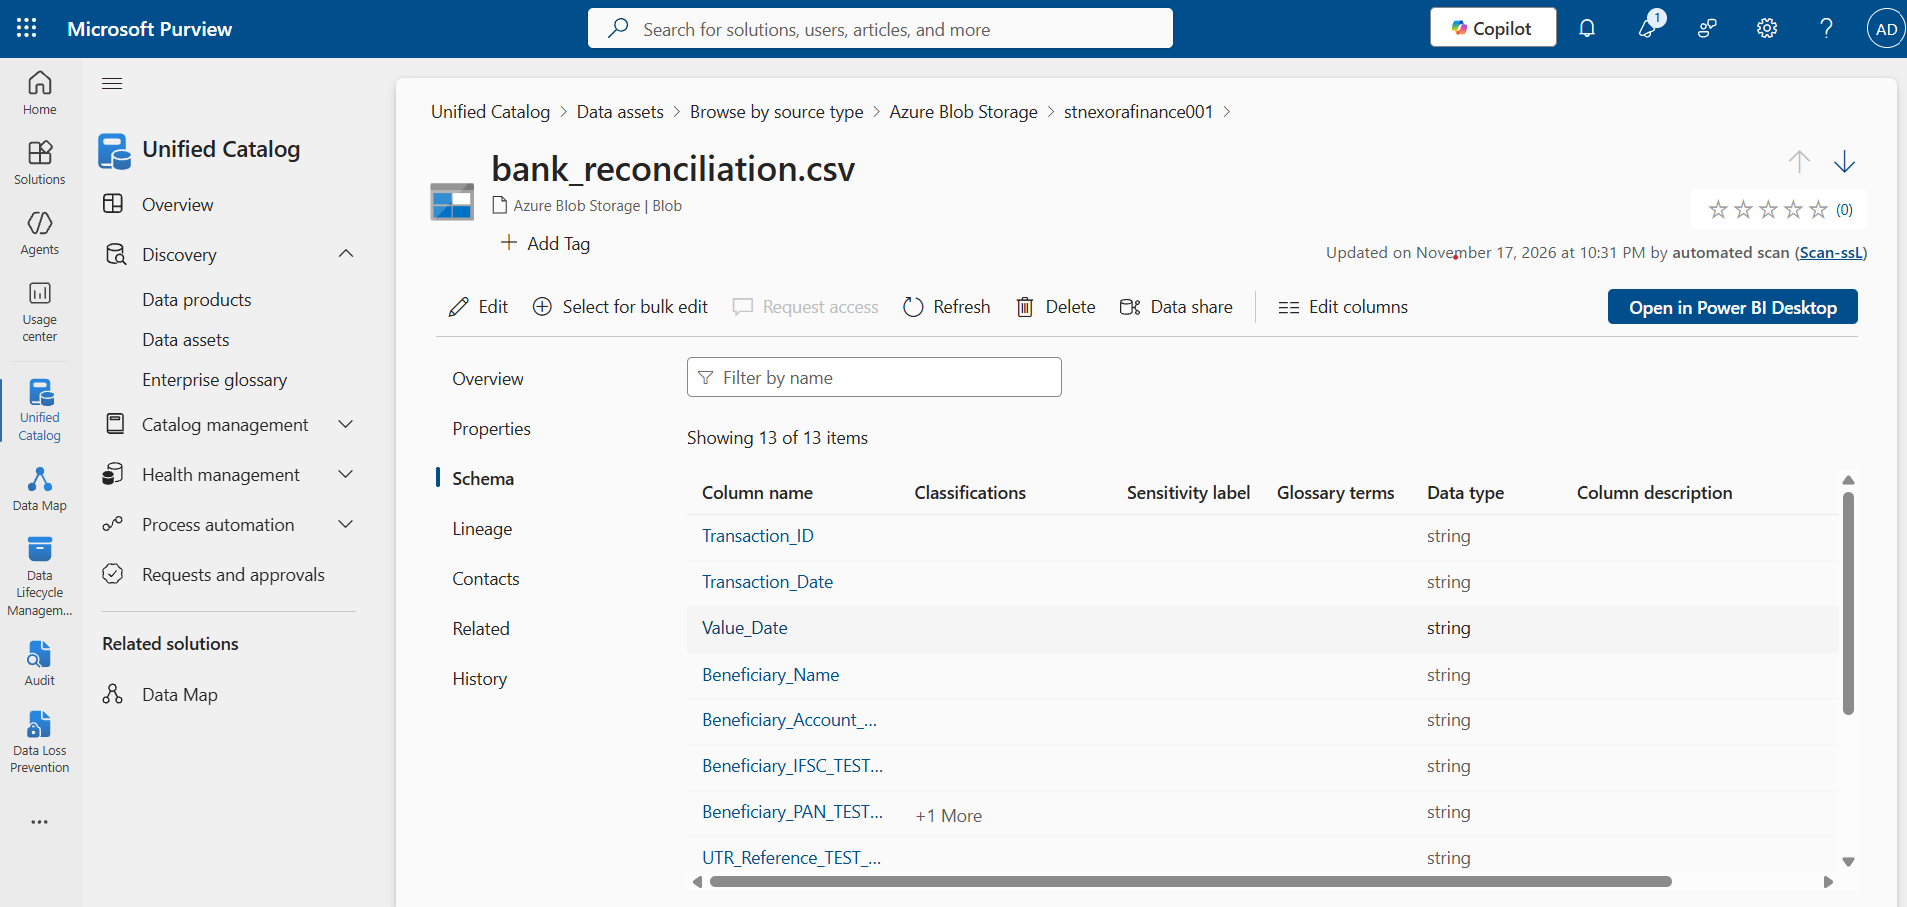
15 — PAN Auto-Classified
04
Act 4 · Screenshots 16–22
Cryptographic Labels, Custom NDIS Regex & Live Leak Prevention
Legal & Security Challenge: Built-in classifiers detect credit cards and national tax IDs, but fail to recognize sector-specific statutory identifiers like Australian NDIS Participant IDs — leaving disability records exposed to accidental external emailing.
16–17
Encrypted Sensitivity Labeling: Engineered custom label
Confidential - PII and Financial at Priority 9 (above Public, General, and Confidential) enforcing cryptographic encryption restricted exclusively to Nexora employees, published to SG-NEX-All-Employees with mandatory justification for any downgrade.18
Custom Statutory NDIS Classifier: Built a custom Sensitive Info Type matching
\bNDIS-\d{3}-\d{3}-\d{3}\b within 300 characters of healthcare keywords (NDIS, Participant, Disability, Plan Manager, Support Coordination) — detecting Australian disability record identifiers that no built-in classifier covers.19
Automated Classification Simulation: Deployed
Nexora-AutoLabel-Confidential-PII across Exchange, SharePoint, and OneDrive, capturing live rule matches to automatically upgrade sensitive files to Confidential - PII and Financial.20–22
Real-Time Exfiltration Blocking (Live Proof): Activated
Nexora-PII-Financial-Leak-Prevention across Exchange, SharePoint, OneDrive, and Teams. When an analyst attempted to email synthetic Indian PAN (ZZZPX5001J), Credit Card (4111111111111111), and NDIS Participant ID (NDIS-430-881-922) to an external Gmail — Outlook blocked the transmission immediately with a policy bounce notice.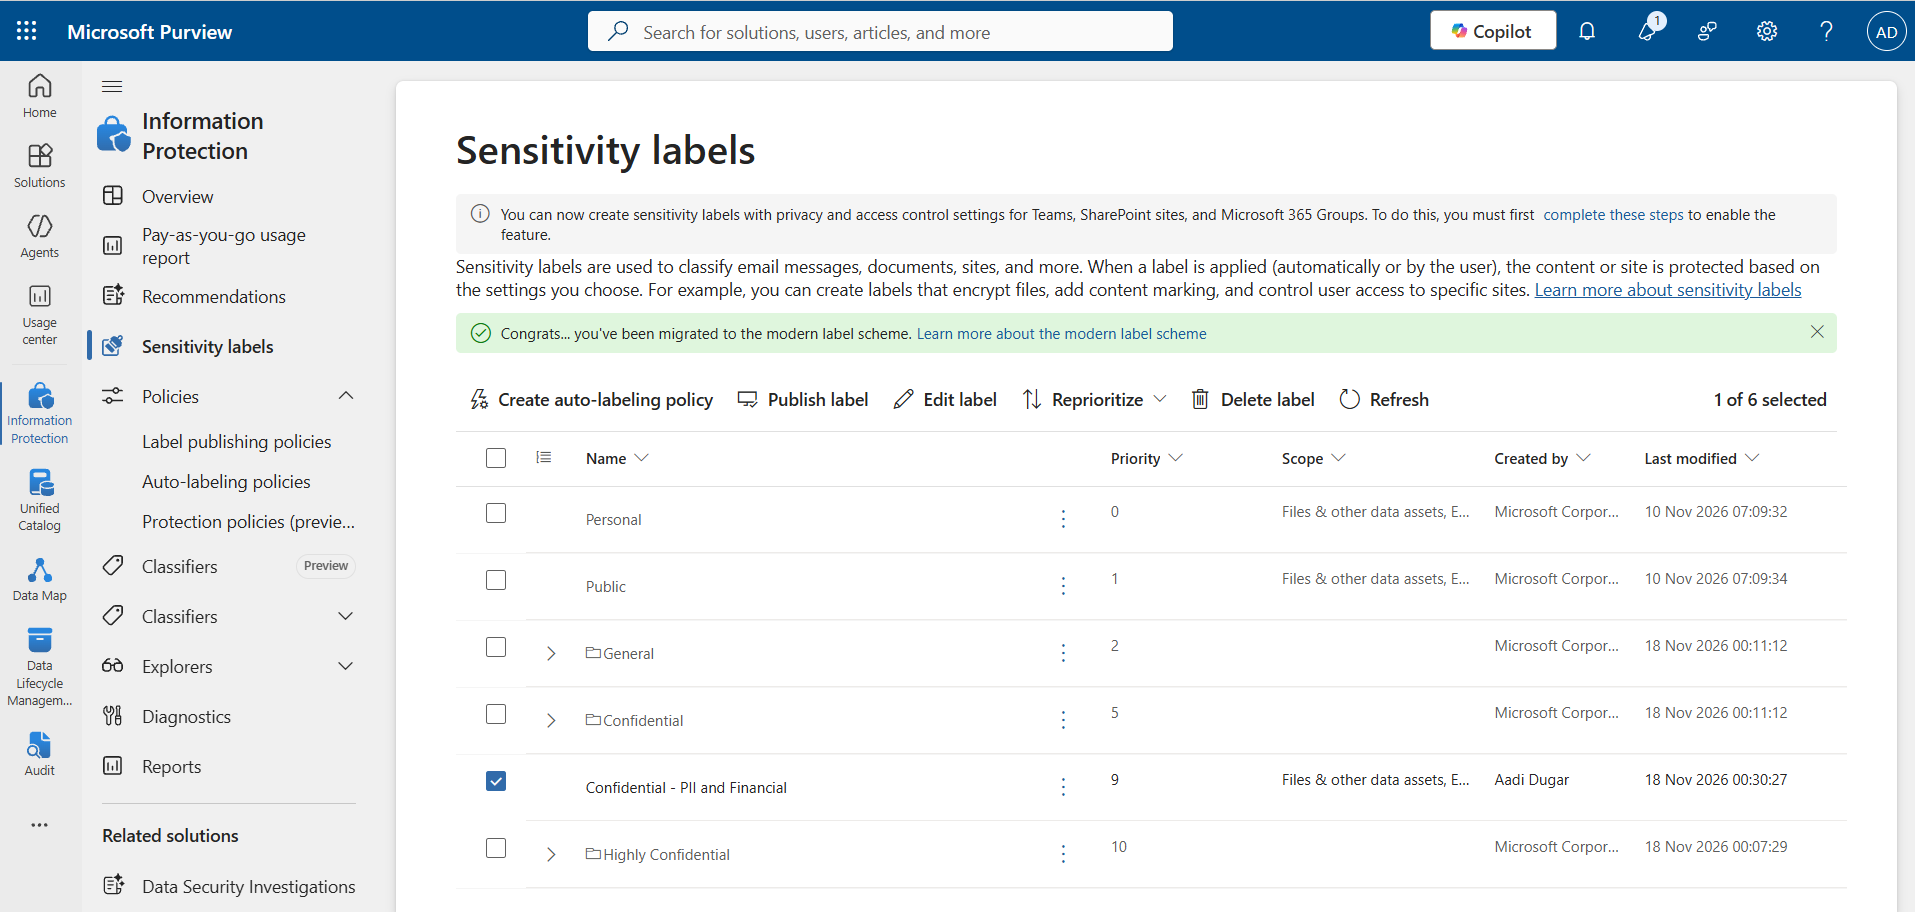
16 — Sensitivity Label Priority 9
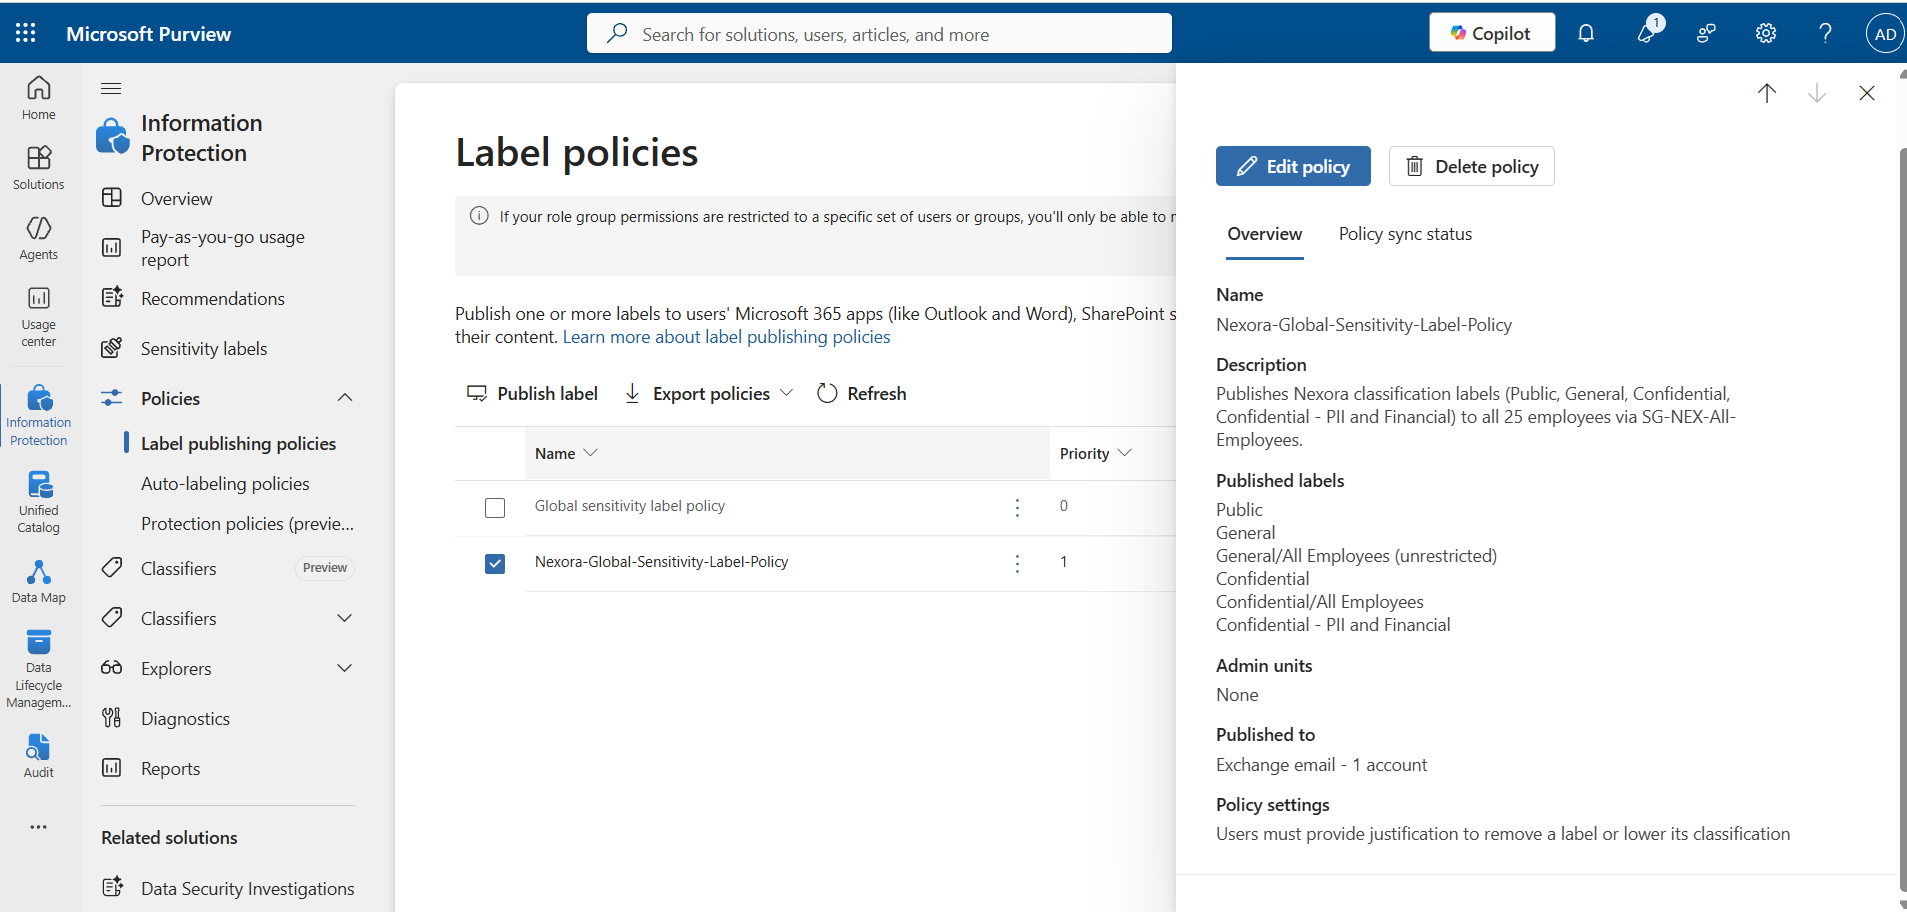
17 — Global Publishing Policy
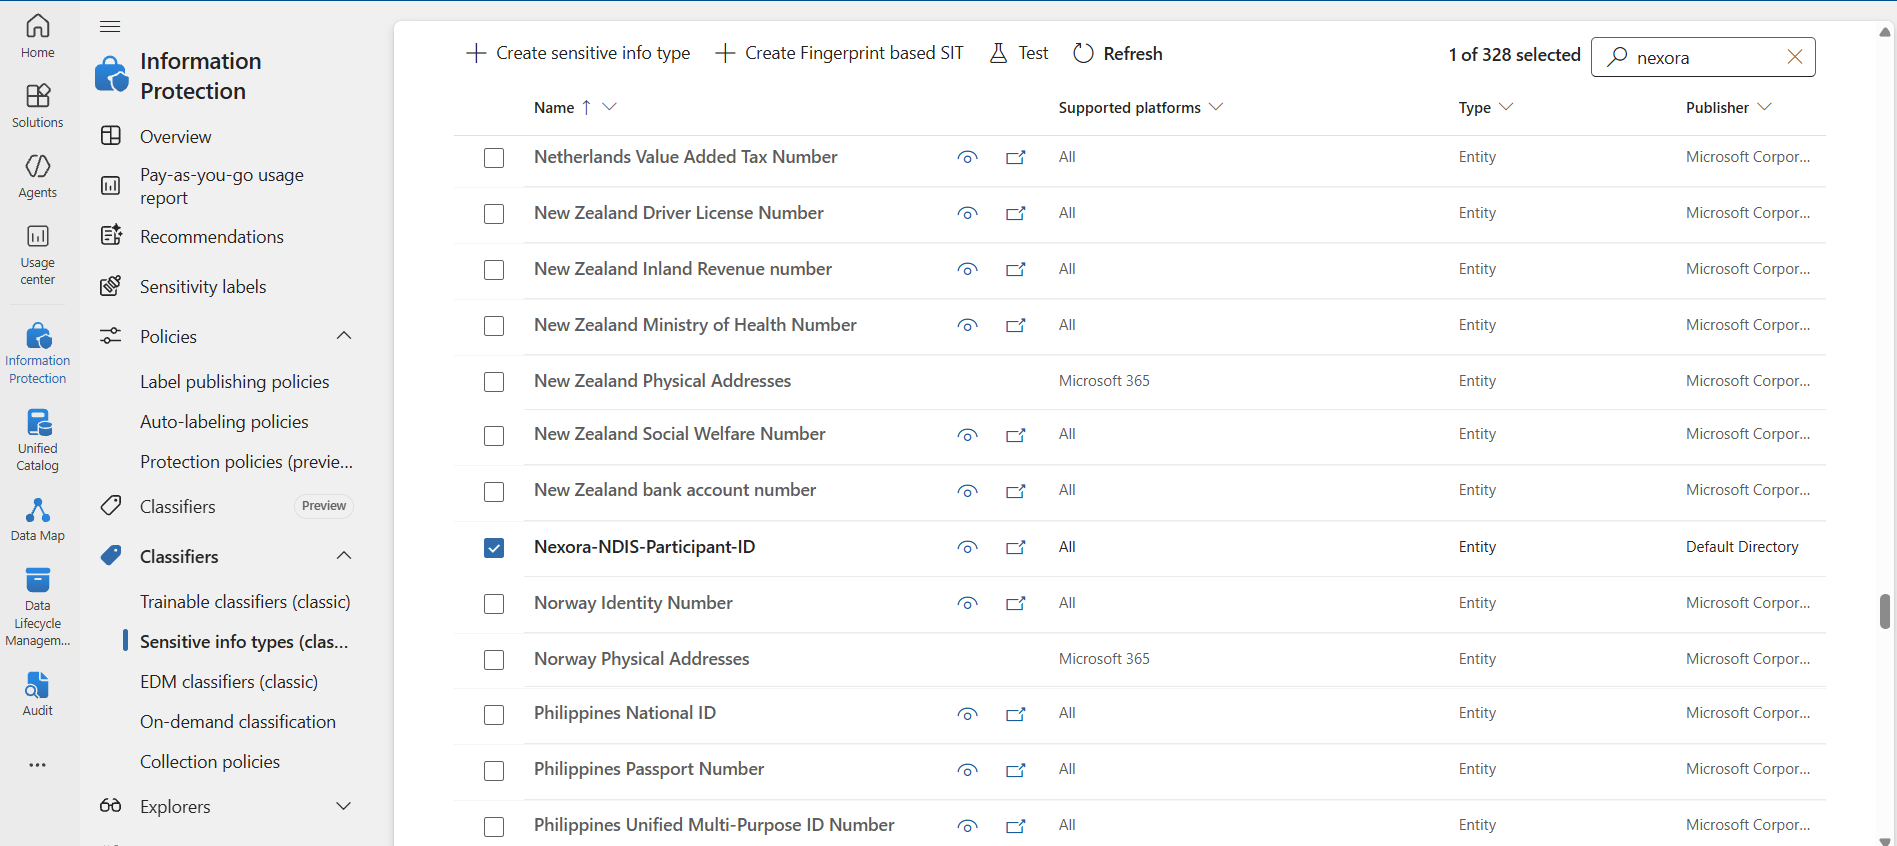
18 — NDIS Regex Classifier
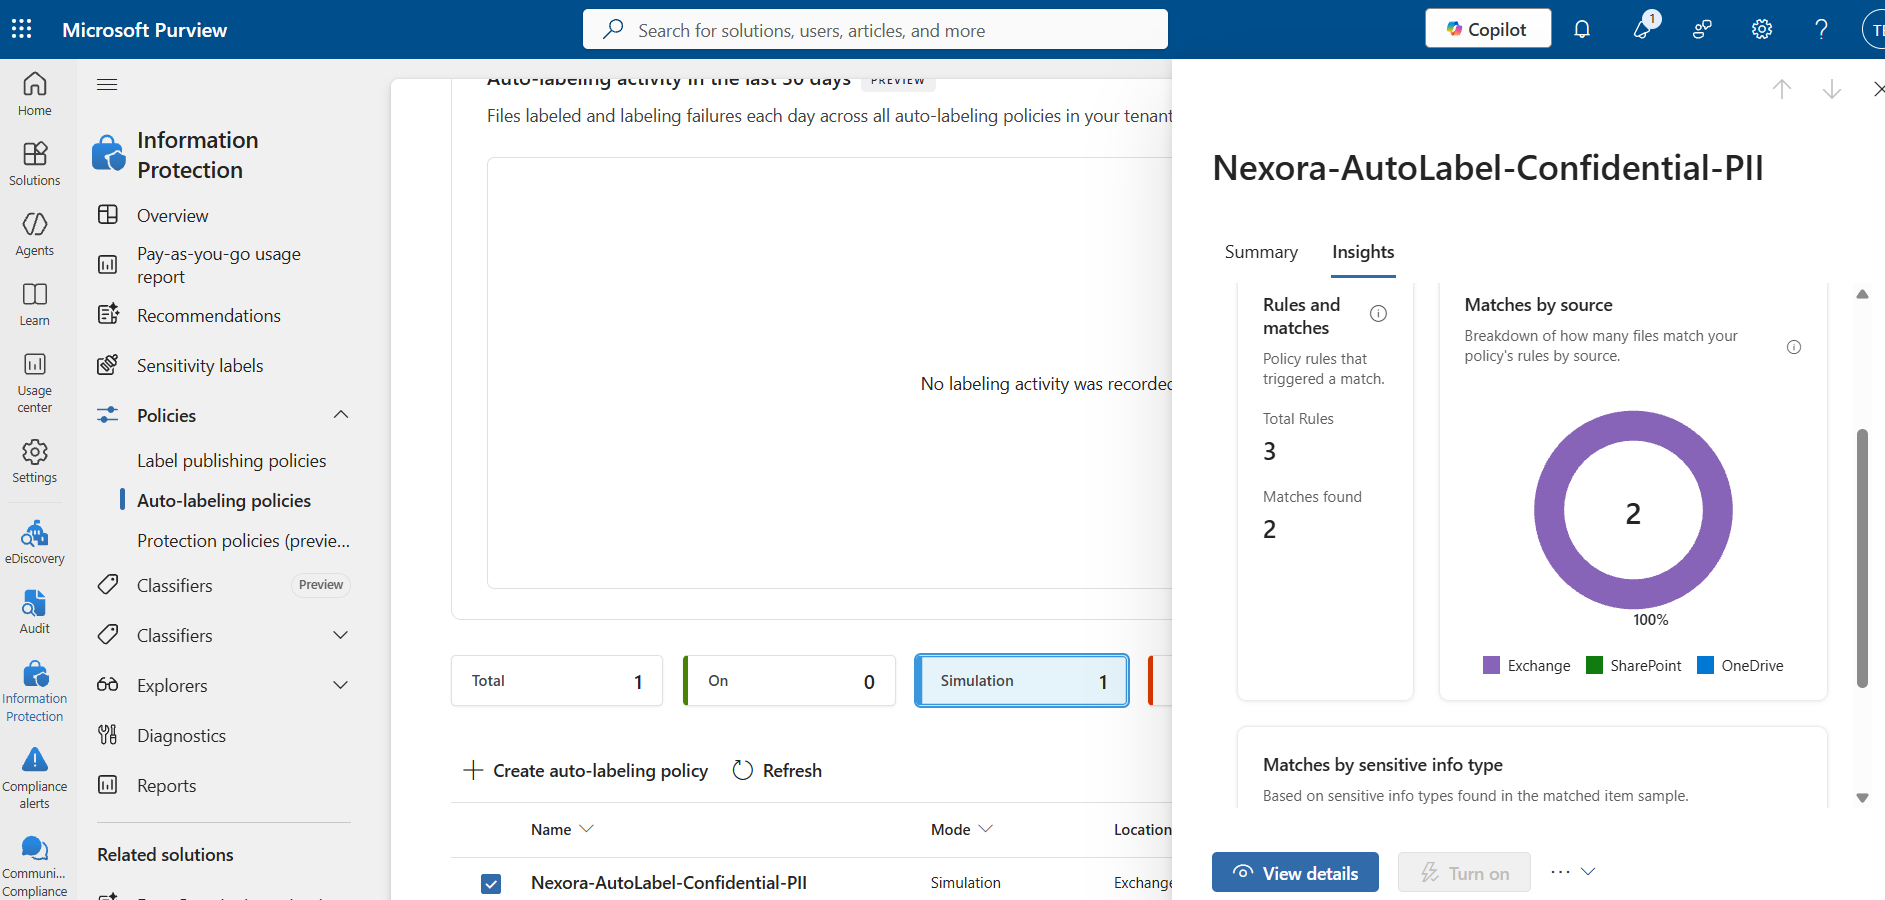
19 — Auto-Label Simulation
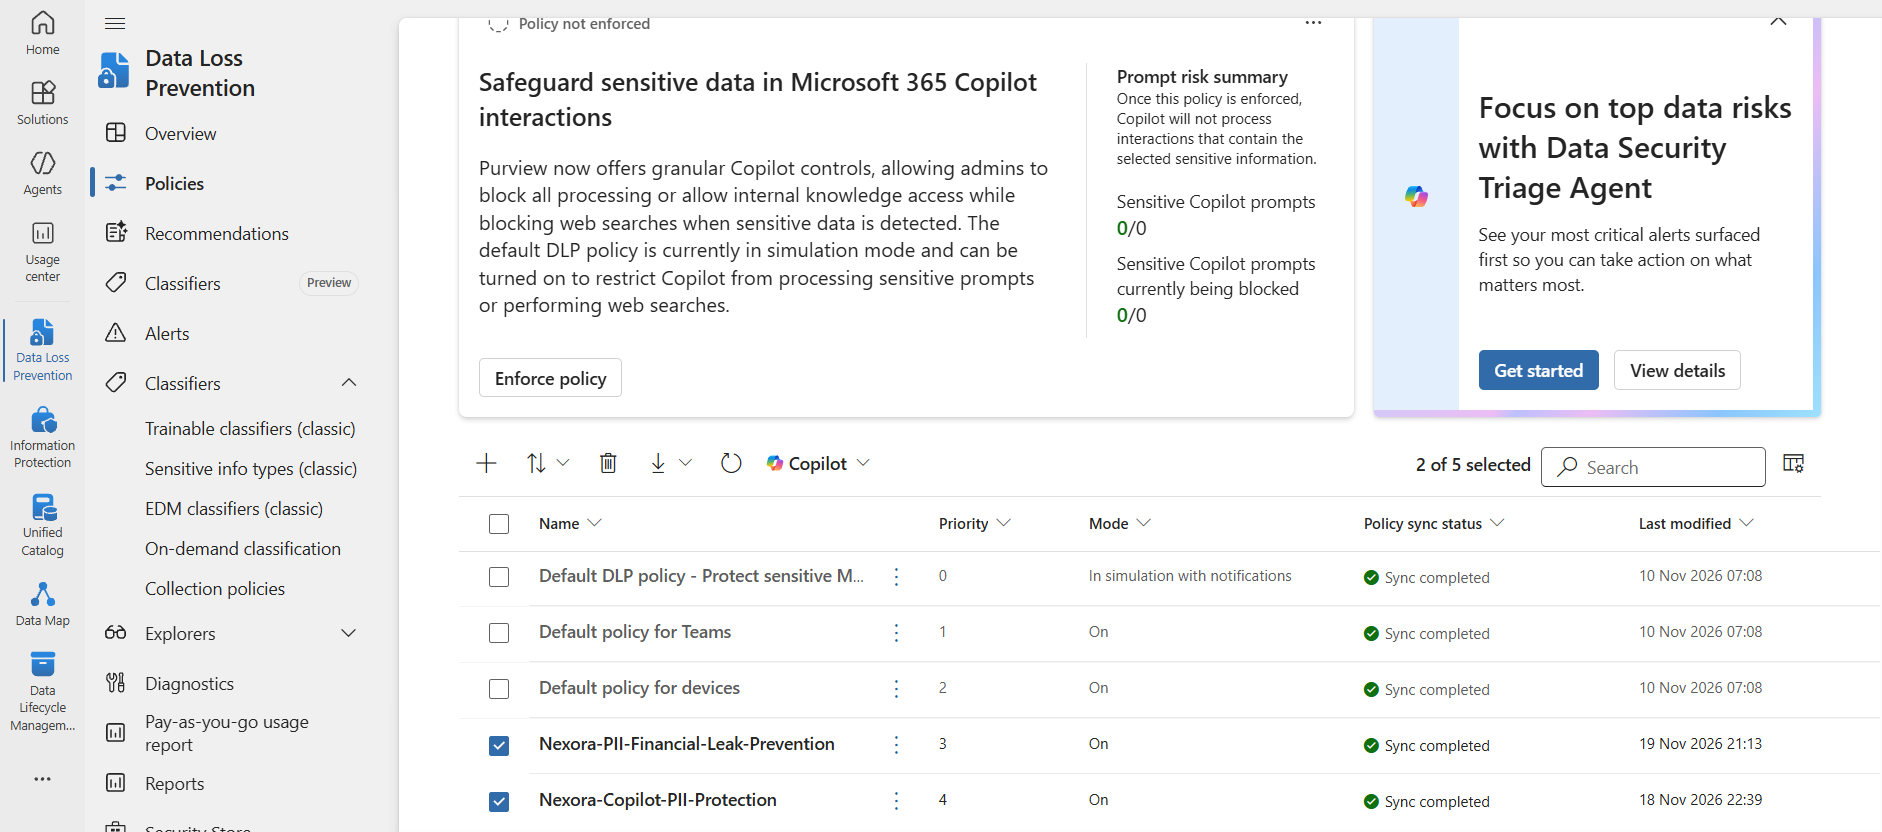
20 — Active DLP Policies
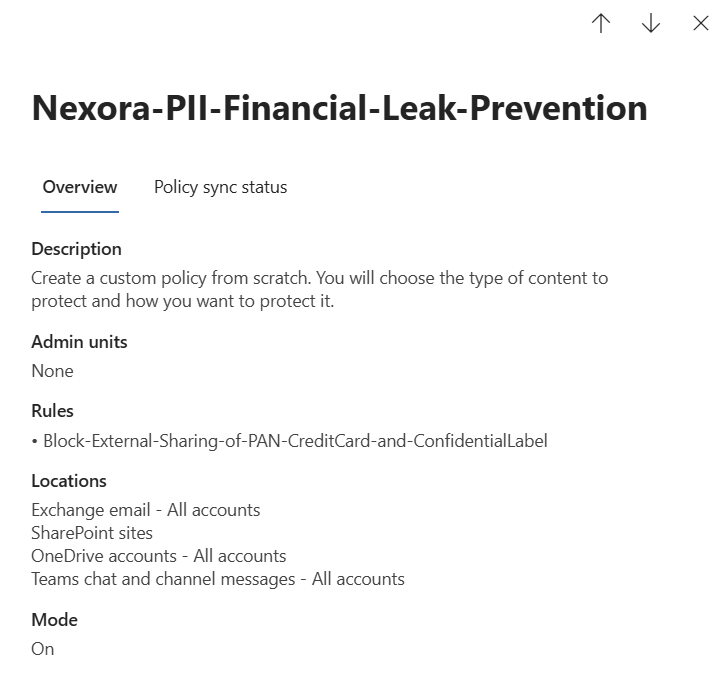
21 — M365 External DLP Rule
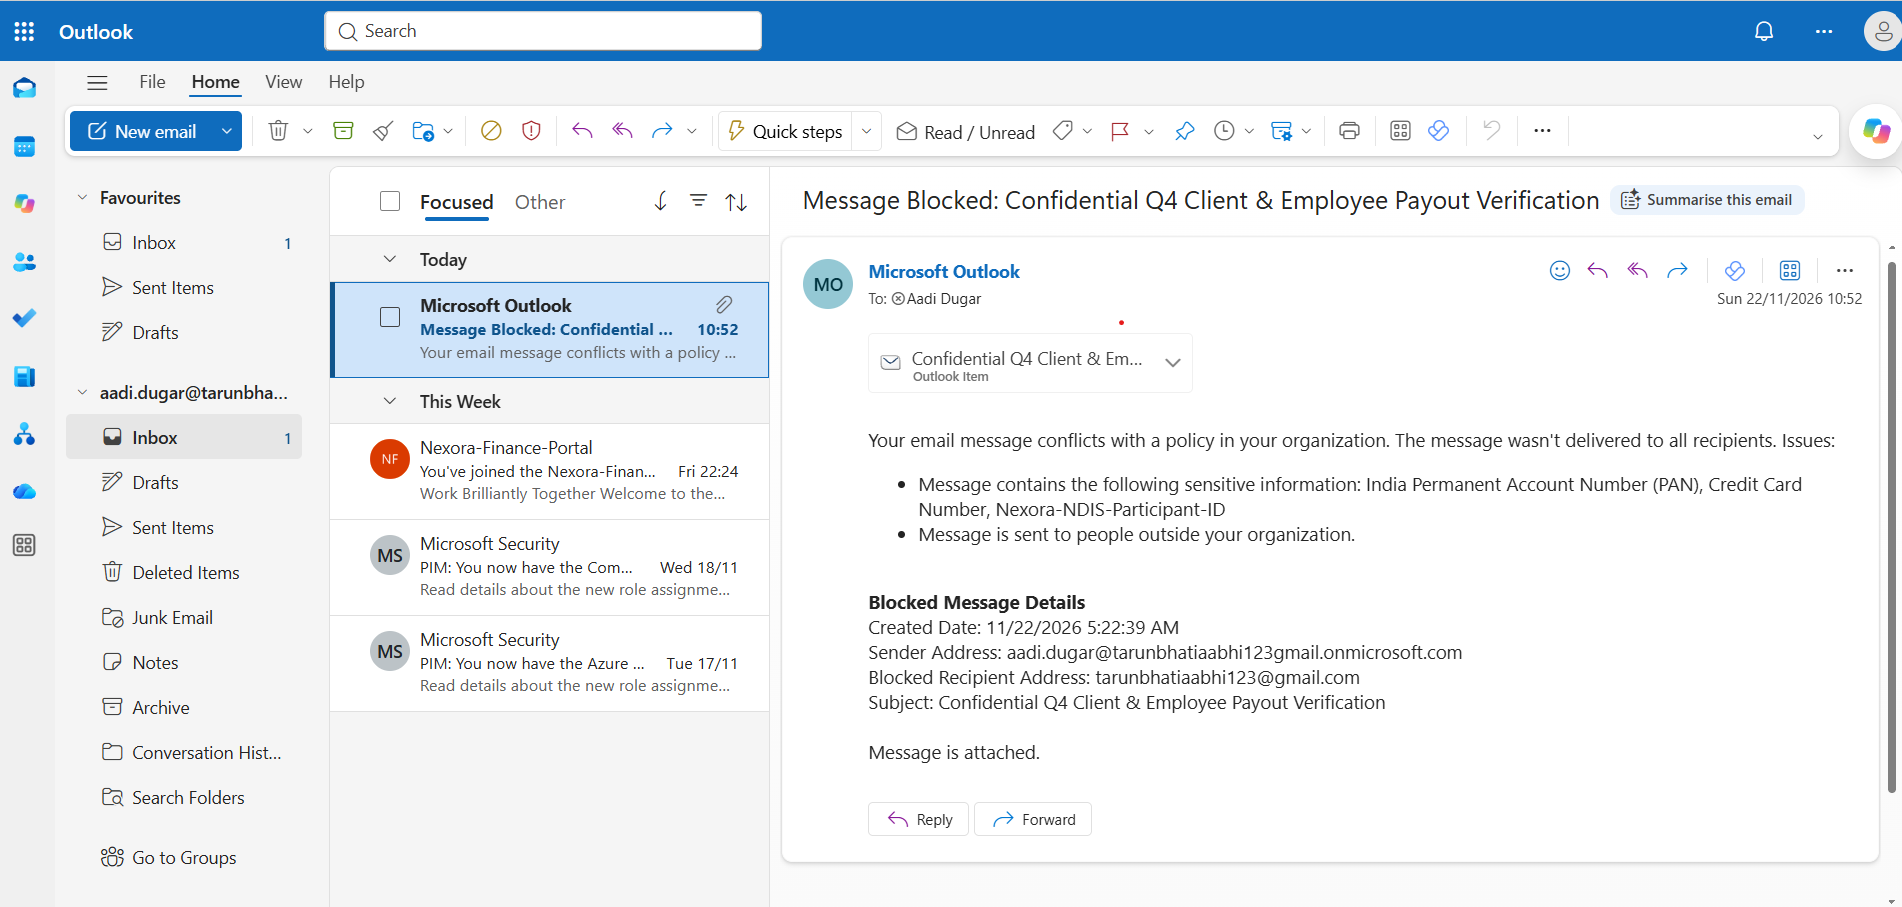
22 — 🔴 Live DLP Block (Outlook)
05
Act 5 · Screenshots 23–24
Copilot & Generative AI Governance
Legal & Security Challenge: Generative AI assistants create a rapid shadow-exfiltration channel when employees paste raw personal data into AI prompts — violating purpose limitation and data minimization duties under DPDP Act Section 6 and APP 6.
23
Dedicated Copilot DLP Guardrail: Activated
Nexora-Copilot-PII-Protection across Microsoft Copilot, Copilot Chat, and Copilot Cowork — blocking AI ingestion of Indian PAN, Credit Card numbers, and Confidential - PII and Financial labelled content. Paired with a formal Generative AI Acceptable Use Policy governing external LLMs (ChatGPT, Gemini, Claude).24
Live Prompt Interception Proof: Tested by pasting synthetic PAN, Credit Card, and NDIS identifiers directly into Microsoft 365 Copilot Chat — Copilot immediately refused processing with an organizational policy restriction alert, proving the guardrail works in real-time.
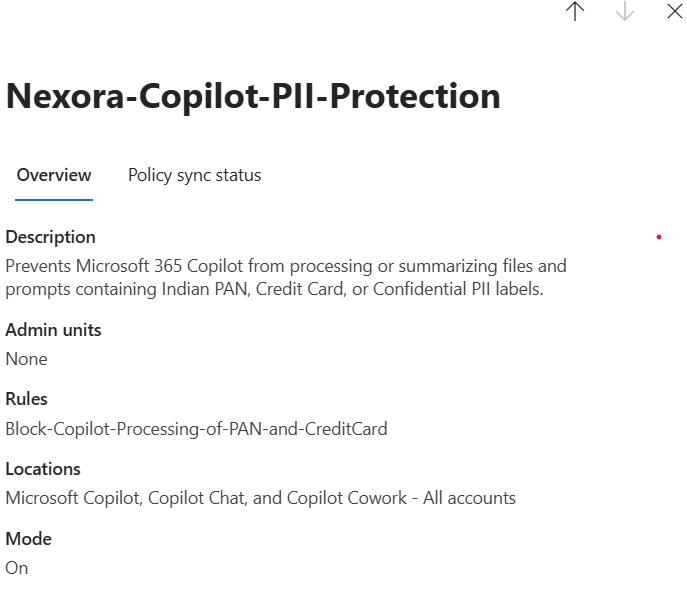
23 — Copilot DLP Policy Config
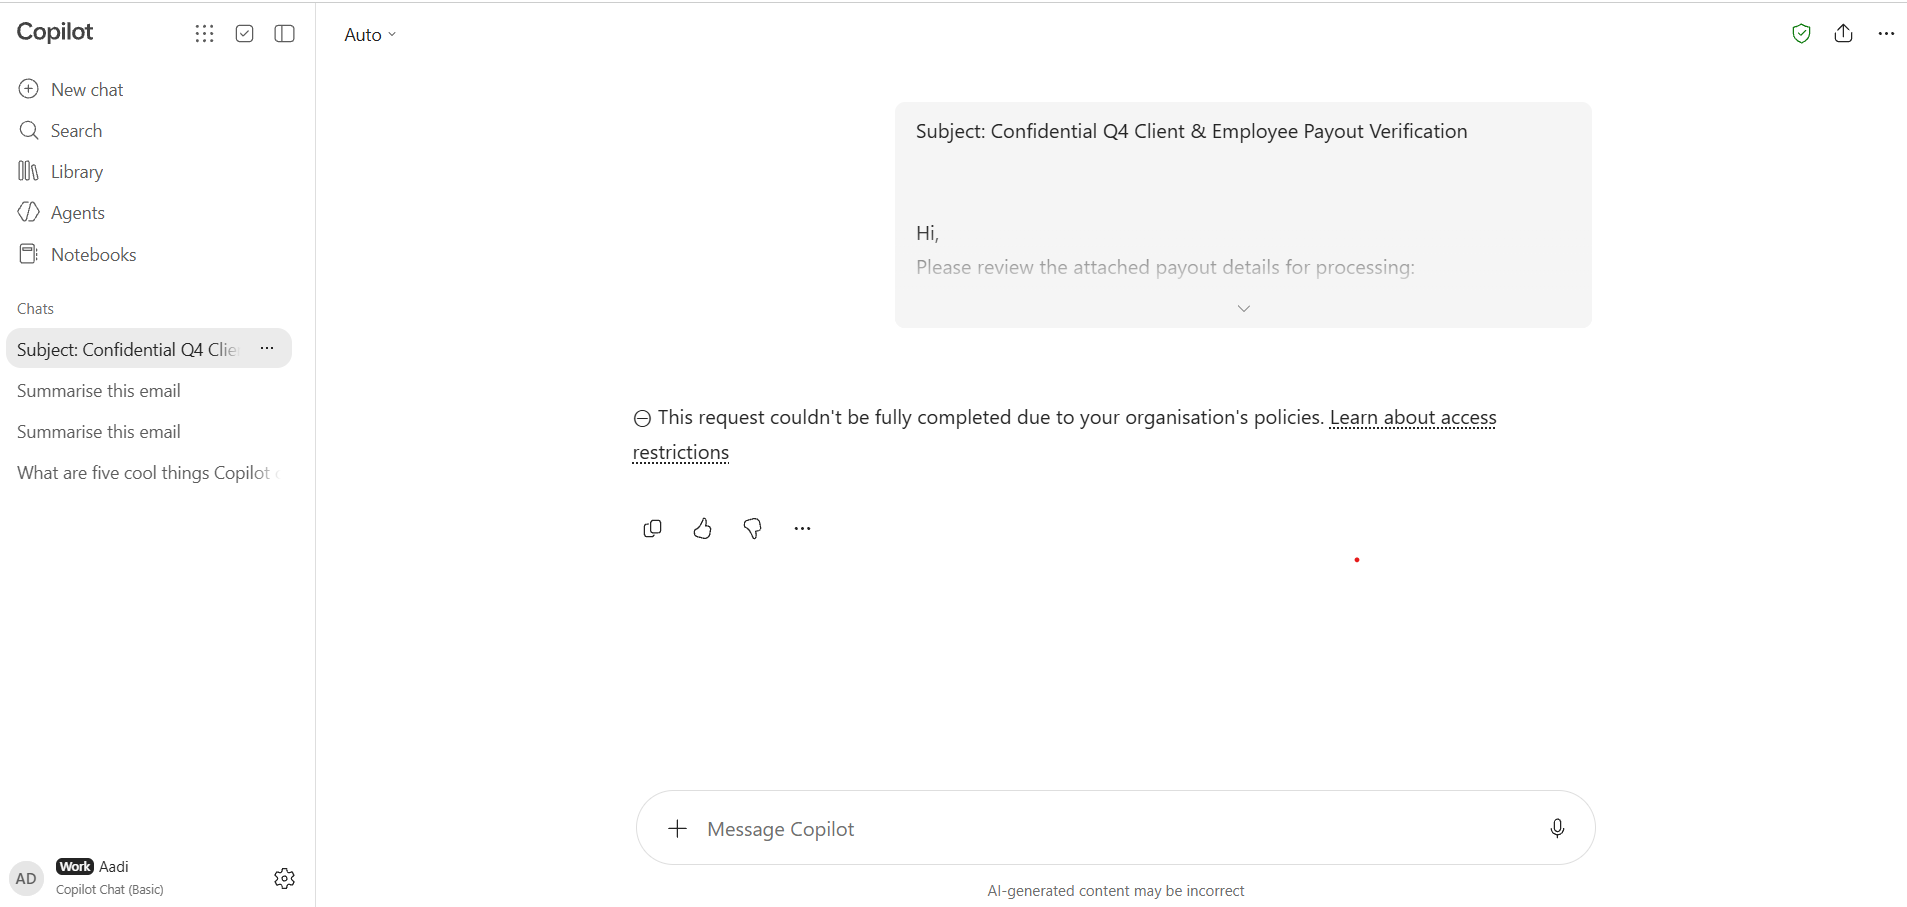
24 — 🔴 Live Copilot Block
06
Act 6 · Screenshots 25–29
Statutory DSAR Fulfillment & Third-Party Redaction
Legal & Security Challenge: Under India's DPDP Act 2023 (Section 11) and Australian APP 12, individuals have the right to access their personal data — but fulfilling an access request must never expose third-party personal data stored inside multi-record corporate spreadsheets.
25
Multi-Record SharePoint Repository: Provisioned private team site
Nexora-Finance-Portal hosting four vendor and financial datasets (bank_reconciliation.csv, card_transactions_test_only.csv, invoice_register.csv, vendor_master.csv).26–27
Targeted DSAR Discovery (DSAR-2026-001): Created Purview eDiscovery (Premium) case
DSAR-2026-001-Vendor-and-Employee-Access-Request and queried Demo Vendor 0002 Group across SharePoint and Exchange — accurately isolating the exact 3 matching files (272,103 bytes) while excluding unrelated card logs.28
Third-Party PII Redaction Governance: Collected all 3 matched CSVs into
DSAR-2026-001-Review-Set, identified unrelated vendors' PAN numbers co-located inside vendor_master.csv, and applied custom tag Requires-Redaction — so third-party records are stripped before external release.29
Case-Sandboxed Reviewer RBAC & Chain-of-Custody Audit: Assigned Purview Role Group Reviewer (backed by SG-NEX-Legal-Compliance) strictly to DSAR-2026-001 — sandboxing reviewers to this single case without raw export privileges — and exported a 4-file DSAR Chain-of-Custody Audit Report (
Summary.csv, Locations.csv, Settings.csv, Statistics.csv) backed by live Unified Audit Logging.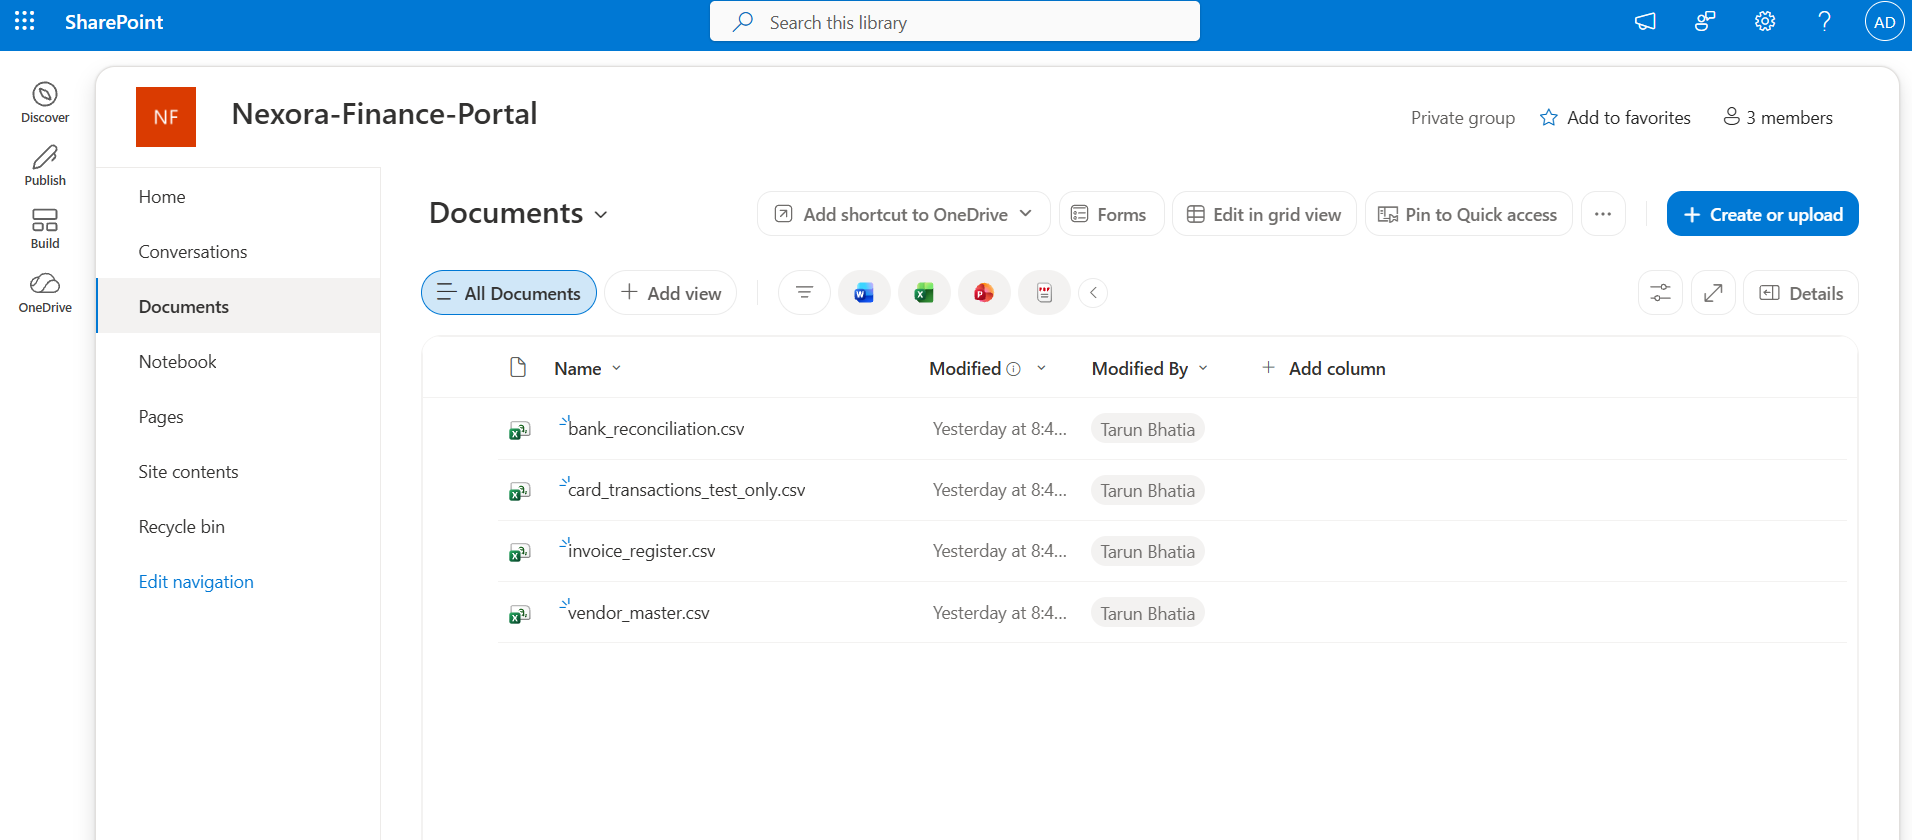
25 — SharePoint Finance Portal
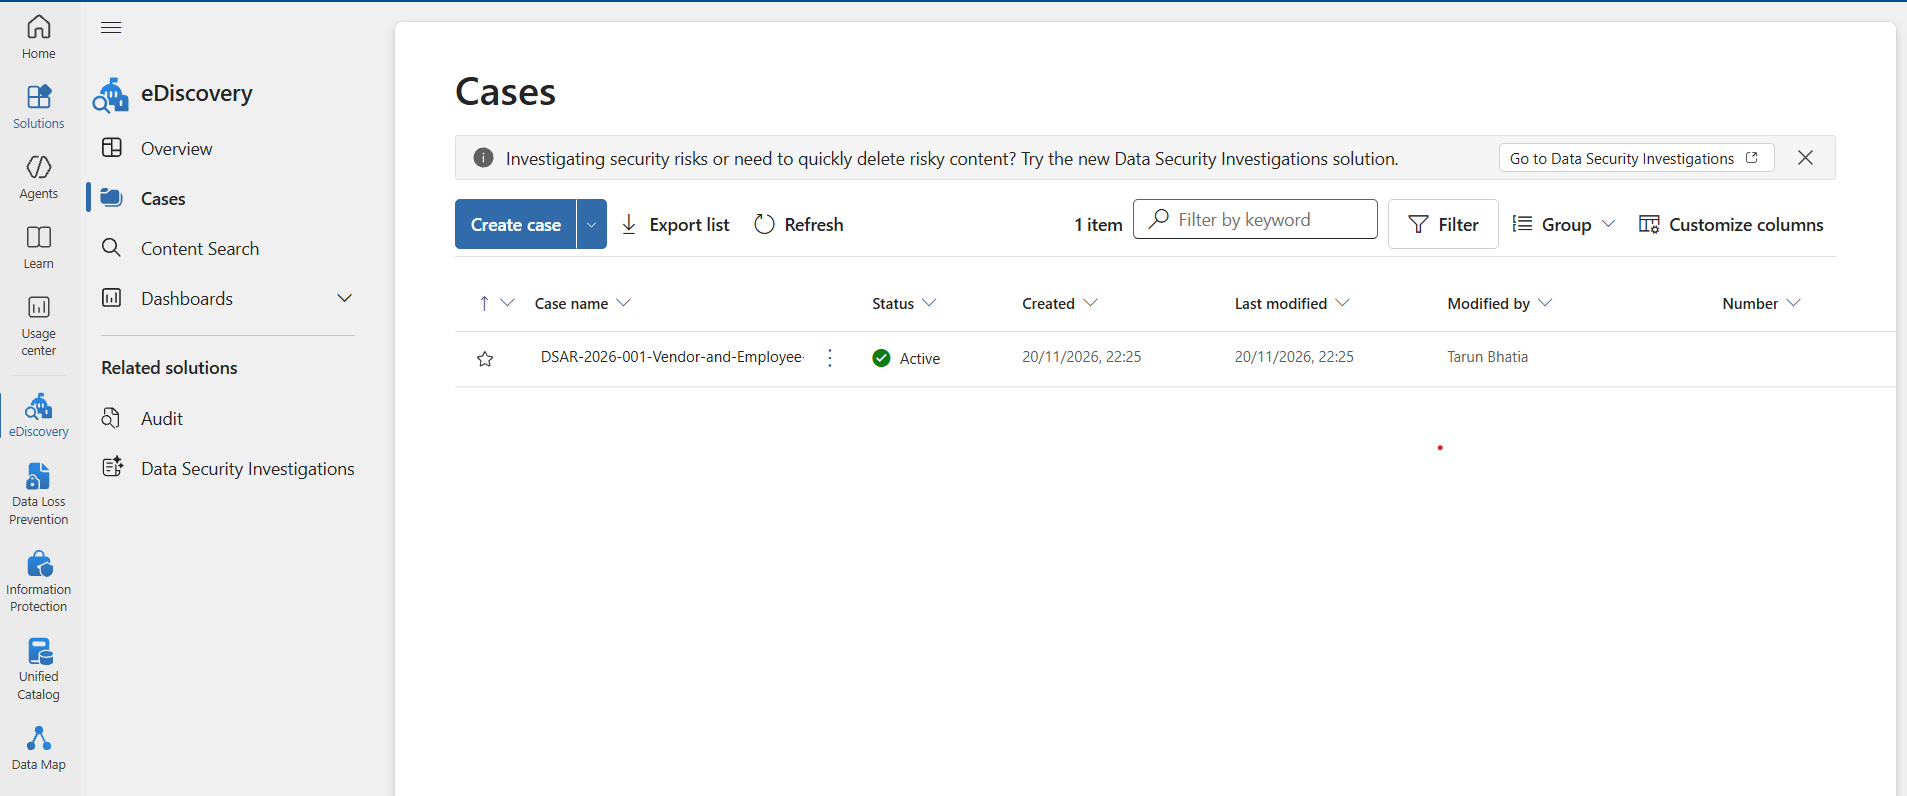
26 — eDiscovery DSAR Case
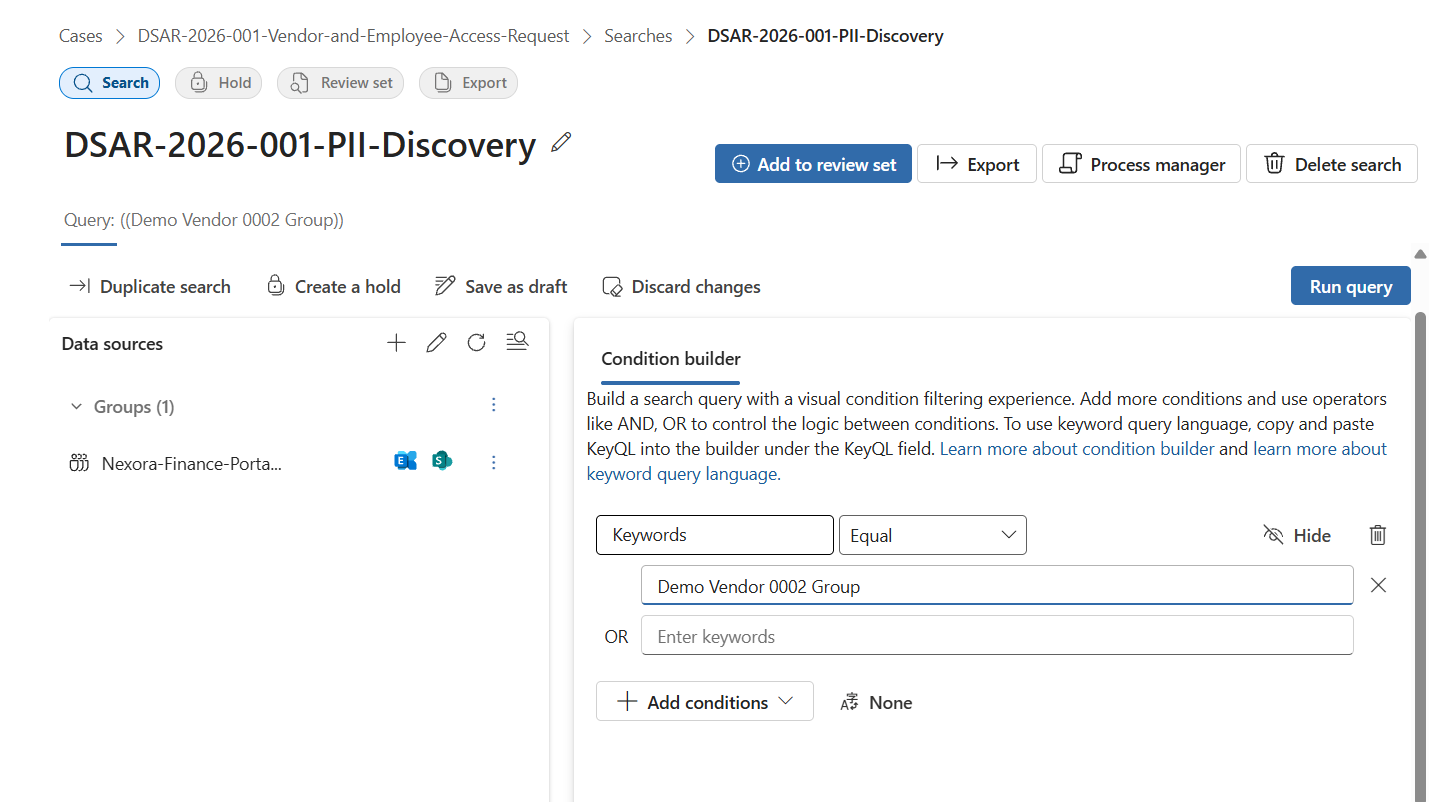
27 — DSAR Search Query
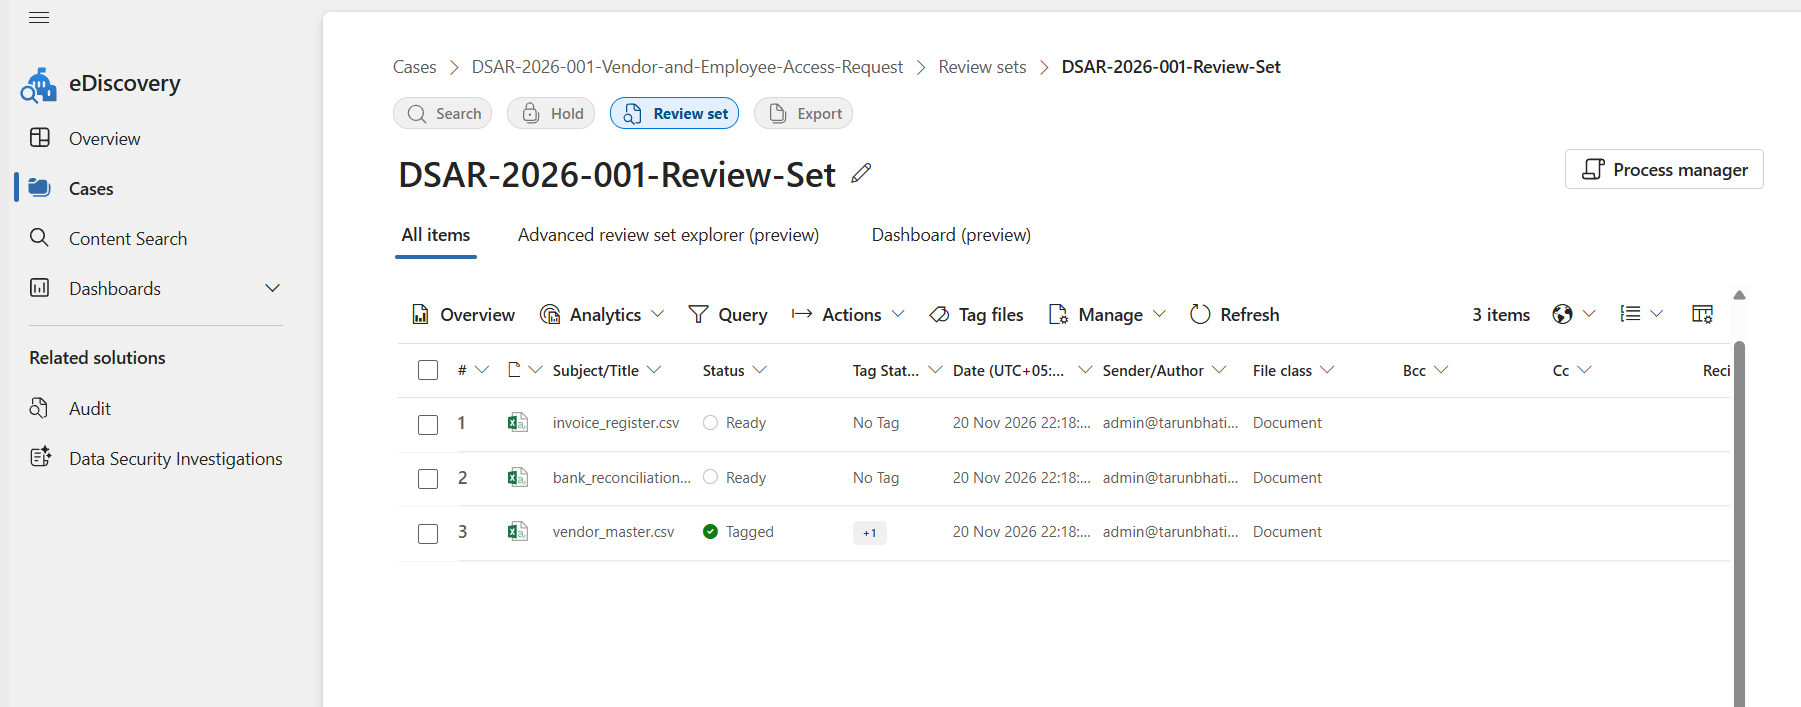
28 — Review Set & Redaction Tag
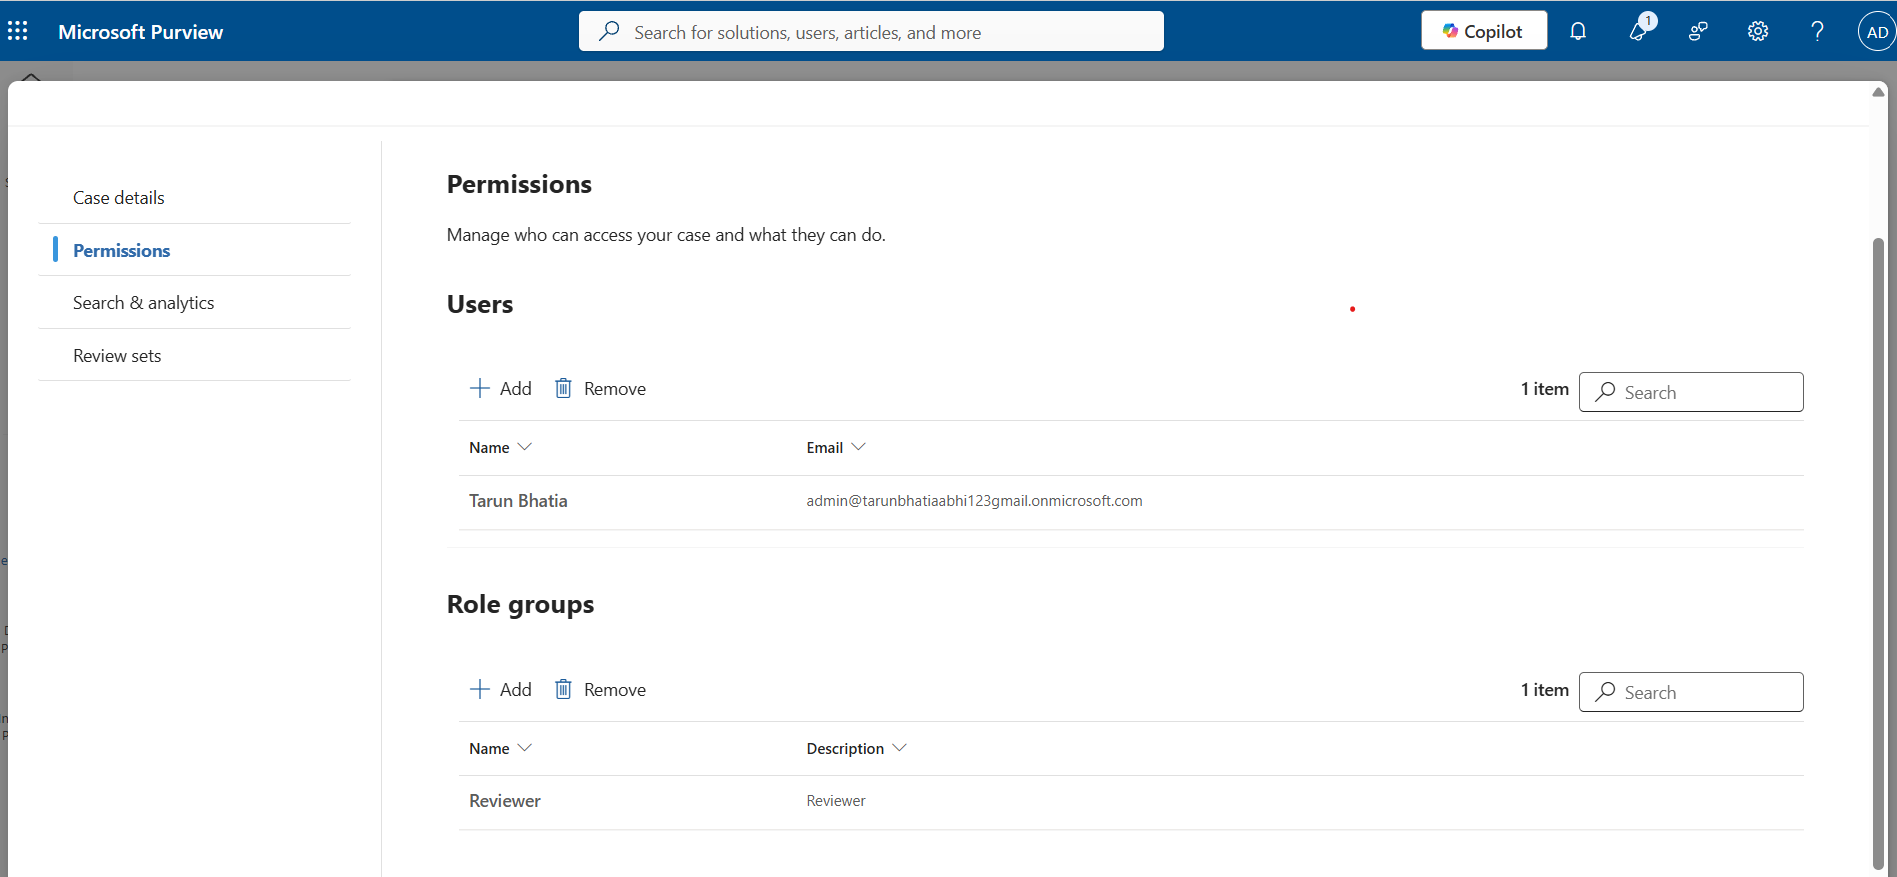
29 — Chain-of-Custody Audit